How to set up single sign-on (SSO)
You will learn
Learn how to set up single sign-on (SSO) for your Klaviyo account or portfolio using an identity provider (IdP).
Why use SSO?
Single sign-on (SSO) helps protect you, as well as your customers, by making your account more secure. If you have SSO set up for your business, you can require your Klaviyo users to log in using their SSO credentials.
Plus, if you use SSO for your organization, you and your users can remain logged in to Klaviyo for a longer period of time before re-entering your credentials.
Before you begin
We strongly suggest reaching out to your company’s IT department to help you set this up because there are certain steps you will need to take within your company’s identity provider. If needed, you can temporarily make them an admin in your account to set up SSO.
Please note:
- You must have a paid plan to use SSO in an account. SSO is also available for portfolios, without a separate paid-plan requirement.
- To follow these steps, sign in as an Owner or Admin for an account, or a Portfolio Owner or Portfolio Admin for a portfolio.
- Users can start SSO from Klaviyo using their workplace ID or custom SSO URL. To let users start from their IdP, turn on IdP initiated log in.
If you use identity provider (IdP) single sign-on (SSO), you can use this to log in to Klaviyo. Security assertion markup language 2.0 (SAML 2.0) SSO gives members access to Klaviyo through an IdP of your choice.
Examples of IdP SSO providers include Okta, OneLogin, Microsoft Entra ID, and more.
If you enforce SSO for all users, any new user will need to accept the invitation and then log in using SSO.
View and use the exemption list
Users added to the exemption list will be able to bypass SSO and log in with a username and password when SSO is enforced for a company. This is important if there is an IdP outage or when you do not want to add a partner, contractor, or agency member to your IdP instance.
You can view the exemption list once SSO is set up. Go to Settings > Security, then under User exemption list, click Set up List or Manage List.
What is a workplace ID?
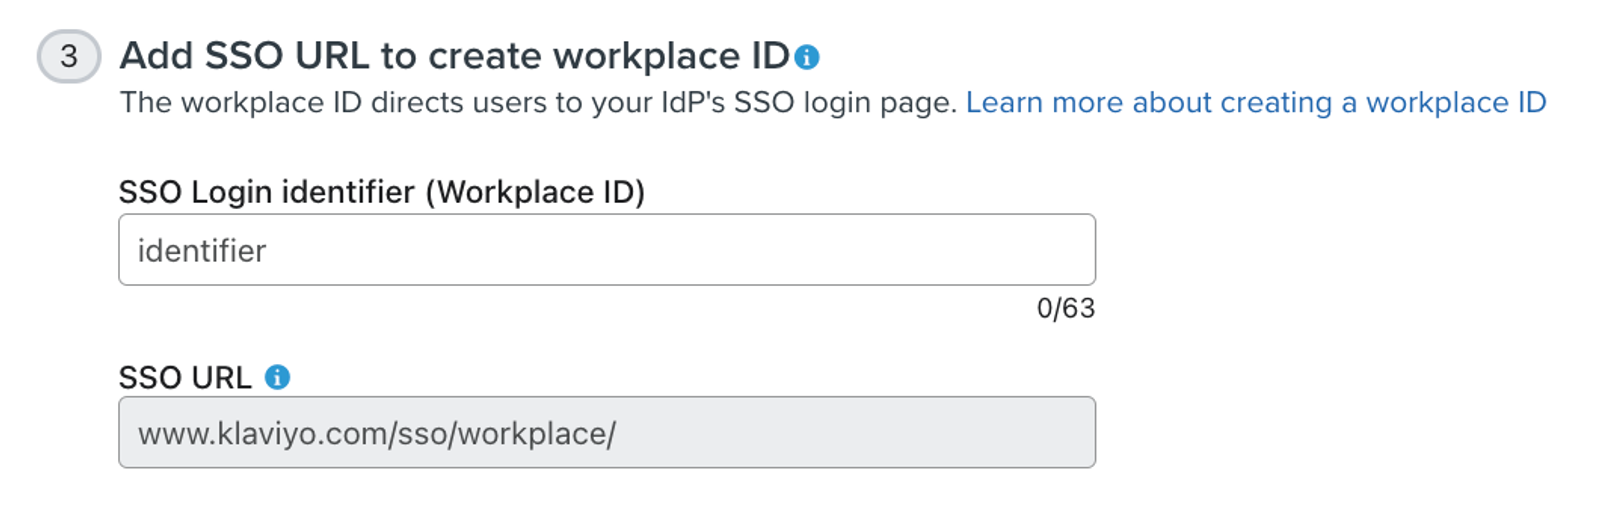
Also called the SSO login identifier, the workplace ID is required to set up SAML SSO in Klaviyo. It is usually the same name as your company. You'll create this ID in step 3 of the SSO configuration page, described under Finish setup in Klaviyo below.
After setting up a workplace ID, users can go directly to your company's custom URL (e.g., www.klaviyo.com/sso/workplace/<id>) to log in to Klaviyo. We recommend telling users to bookmark this URL to speed up the login process.
Tips for creating a workplace ID:
- The ID must be unique and 3–63 characters long.
- The ID can contain only upper- or lowercase letters, numbers, hyphens (-), and underscores (_).
- The ID should be simple and easy for users to remember (such as your company name).
- For example, Klaviyo’s workplace ID is “Klaviyo.”
About just-in-time (JIT) provisioning
Just-in-time (JIT) provisioning is enabled when you first save a new SSO configuration. You can turn it off in Settings > Security. When a user is added to an account with JIT provisioning, the user will need to accept the invite in their email to start accessing the account.
When SSO and JIT provisioning are on, manage the user's Klaviyo role in your IdP. Users on the exemption list can still have their roles changed in Klaviyo, and the Owner can still transfer ownership in Klaviyo. For other users, changing roles in Klaviyo requires turning off JIT and, if enabled, SCIM. If you turn JIT back on, the role sent by your IdP can update the user's role again at their next SSO login.
What is JIT?
When JIT provisioning is enabled, IT admins no longer need to create accounts manually for each user in each of their applications. Instead, user accounts are created the first time users try to log in to an application, as long as the user has permission for that app.
For instance, IT admins can automatically grant Klaviyo access to all users in their IdP so that those users' accounts will automatically be created the first time they log in to Klaviyo via their SSO portal or through Klaviyo-initiated login.
Set up SAML SSO
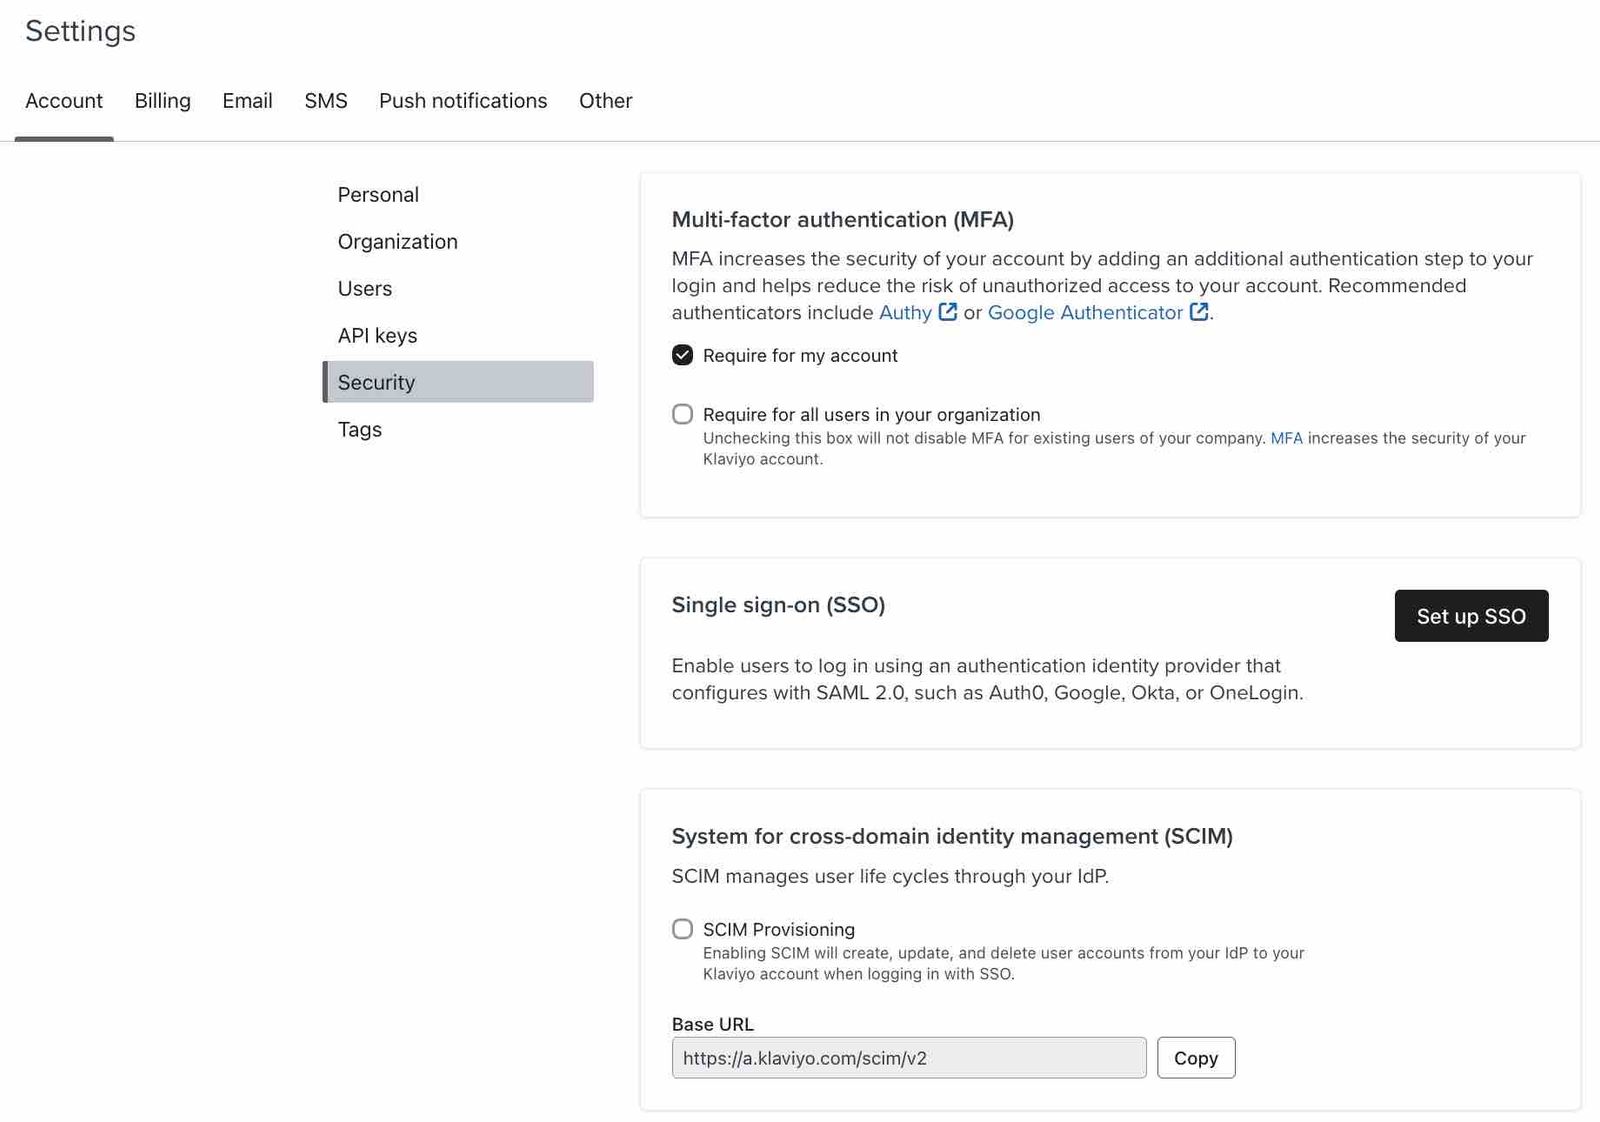
- In Klaviyo, click your organization name in the bottom left corner.
- Click Settings.
- Select Security.
- Click Set up SSO. (Note that multi-factor authentication is not required.)
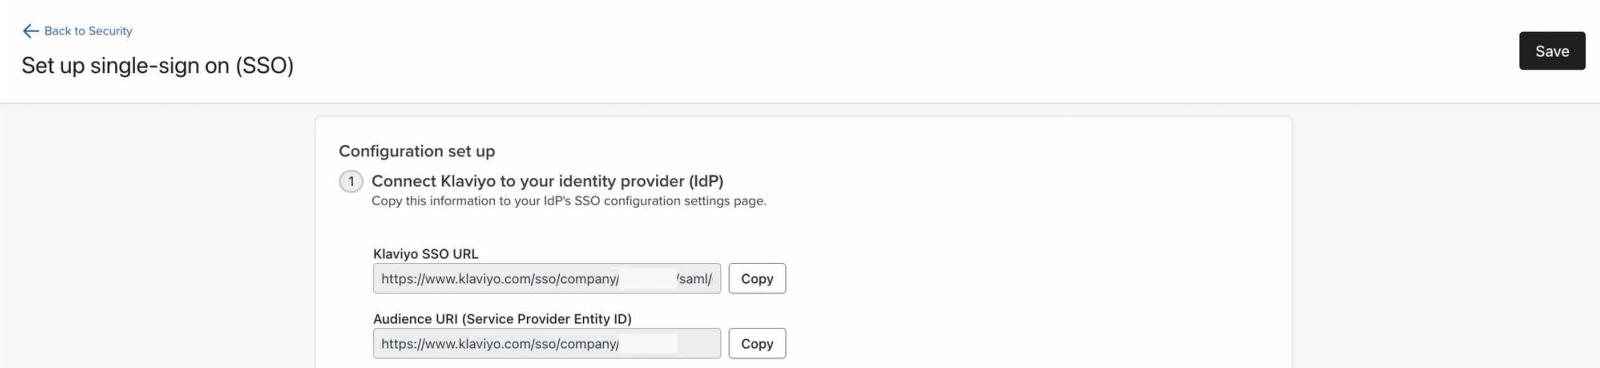
- Copy the Klaviyo SSO URL and Audience URI (Service Provider Entity ID) for use in the next section.
Log in to your SSO provider
Open the dropdowns below for IdP-specific instructions. For current provider navigation, see Okta’s SAML app integration guide or Microsoft’s SAML SSO guide. In general, you will need to:
- Open a new tab and log in to your SSO provider.
- Find the SAML configuration settings for your provider.
- Paste in both the Klaviyo SSO URL and Audience URI (Service Provider Entity ID) in the corresponding fields, then save.
- Download or locate your IdP’s metadata.
- Assign users and their roles to the Klaviyo app, including the person who will test SSO.
- To create users with JIT provisioning, configure your IdP to send a SAML attribute named role with the appropriate Klaviyo role key below. We recommend using the key format because some IdPs convert attributes to lowercase, so the label format is not recommended.
Account user roles | Portfolio user roles |
owner | portfolio_owner |
admin | portfolio_admin |
manager | portfolio_manager |
analyst | portfolio_analyst |
campaign_coordinator | |
content_creator | |
support |
The roles depend on the type of account where you're setting up SSO. In a normal account, only account user roles are applicable. In a portfolio account, only portfolio user roles are applicable.
Use owner or portfolio_owner only for the existing Owner. JIT provisioning cannot create an Owner or transfer ownership. Transfer ownership in Klaviyo instead.
Okta
- Log in to your Okta admin account.
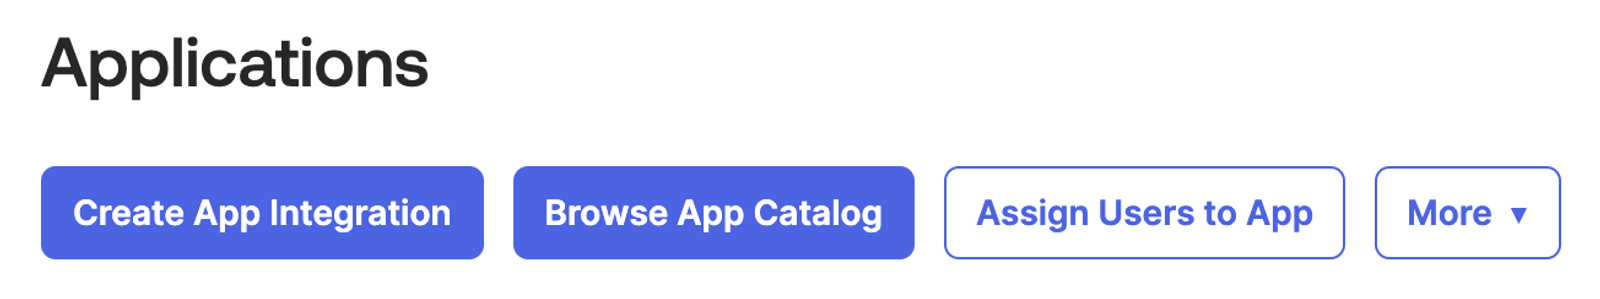
- Navigate to Applications and Resources > Applications.
- Select Create App Integration, then Classic experience.
- In the modal, select the option for SAML 2.0.
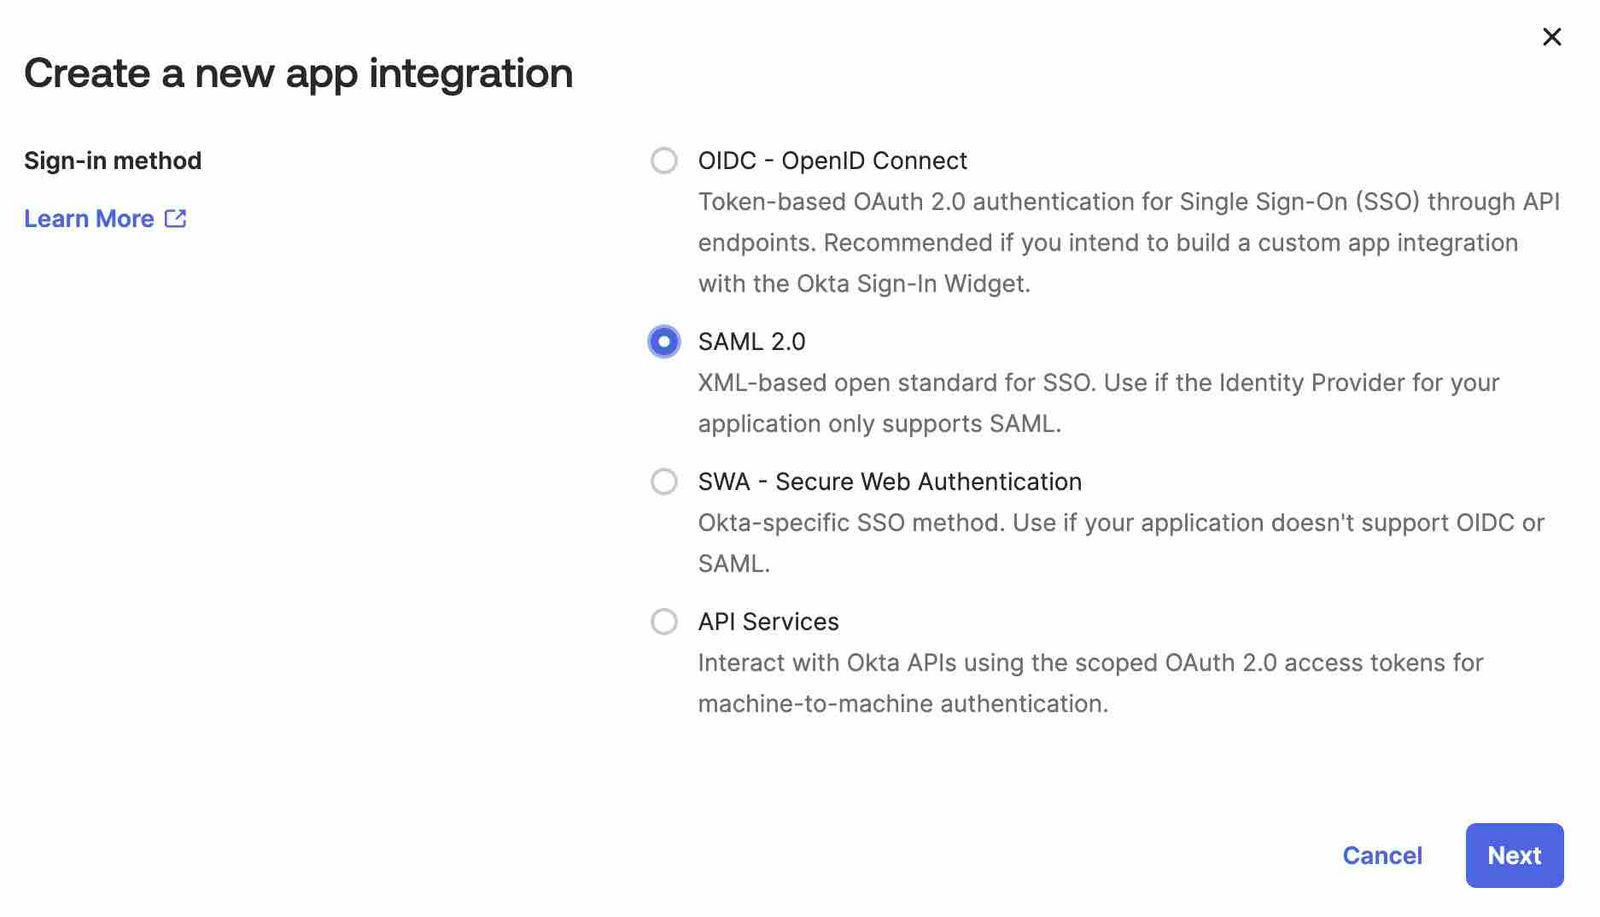
- Click Next.
- Name the integration (e.g., “Klaviyo”).
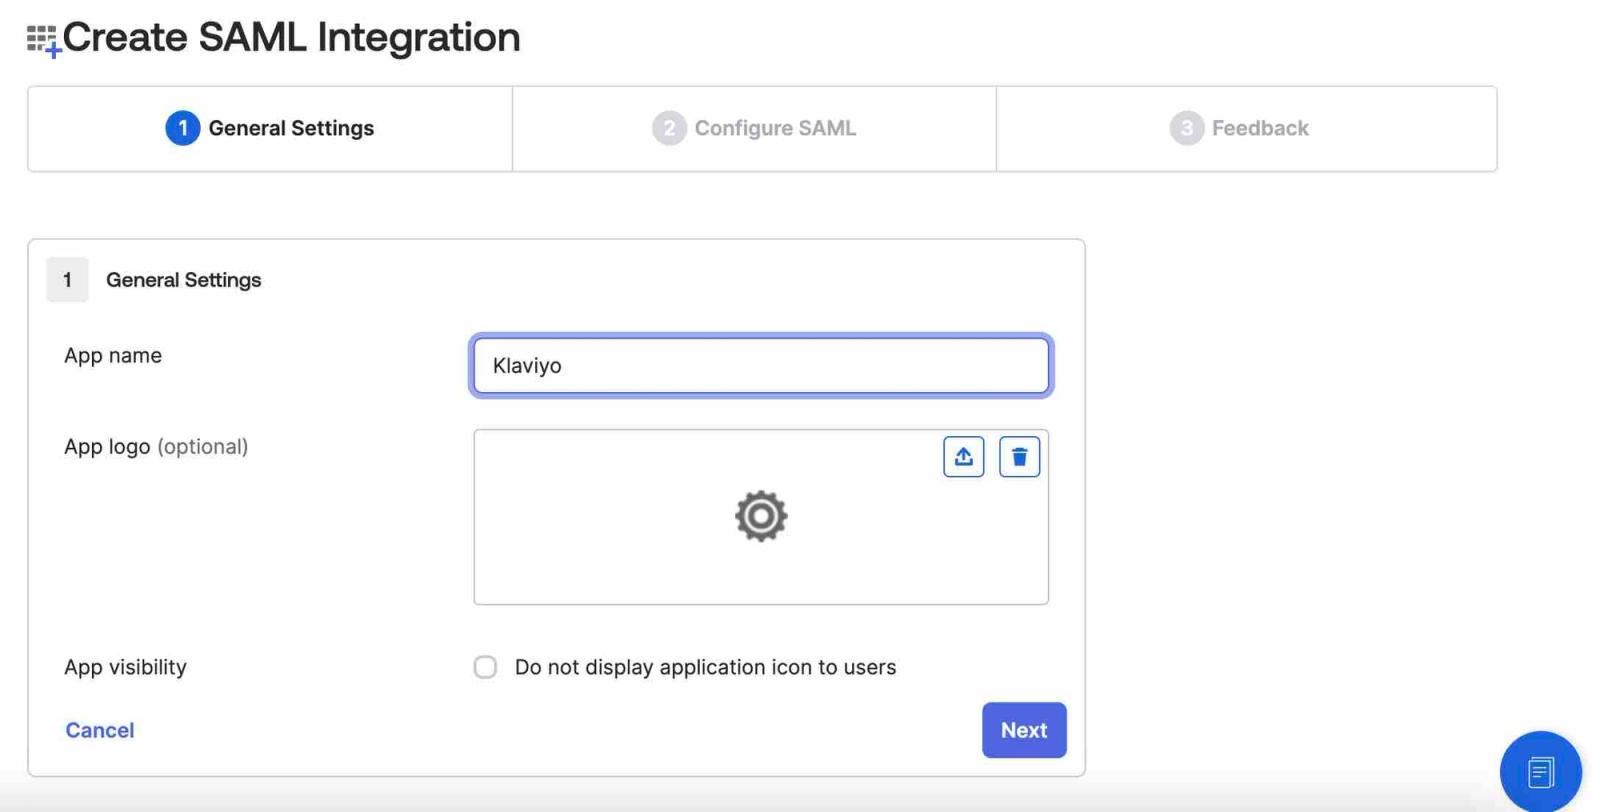
- Click Next.
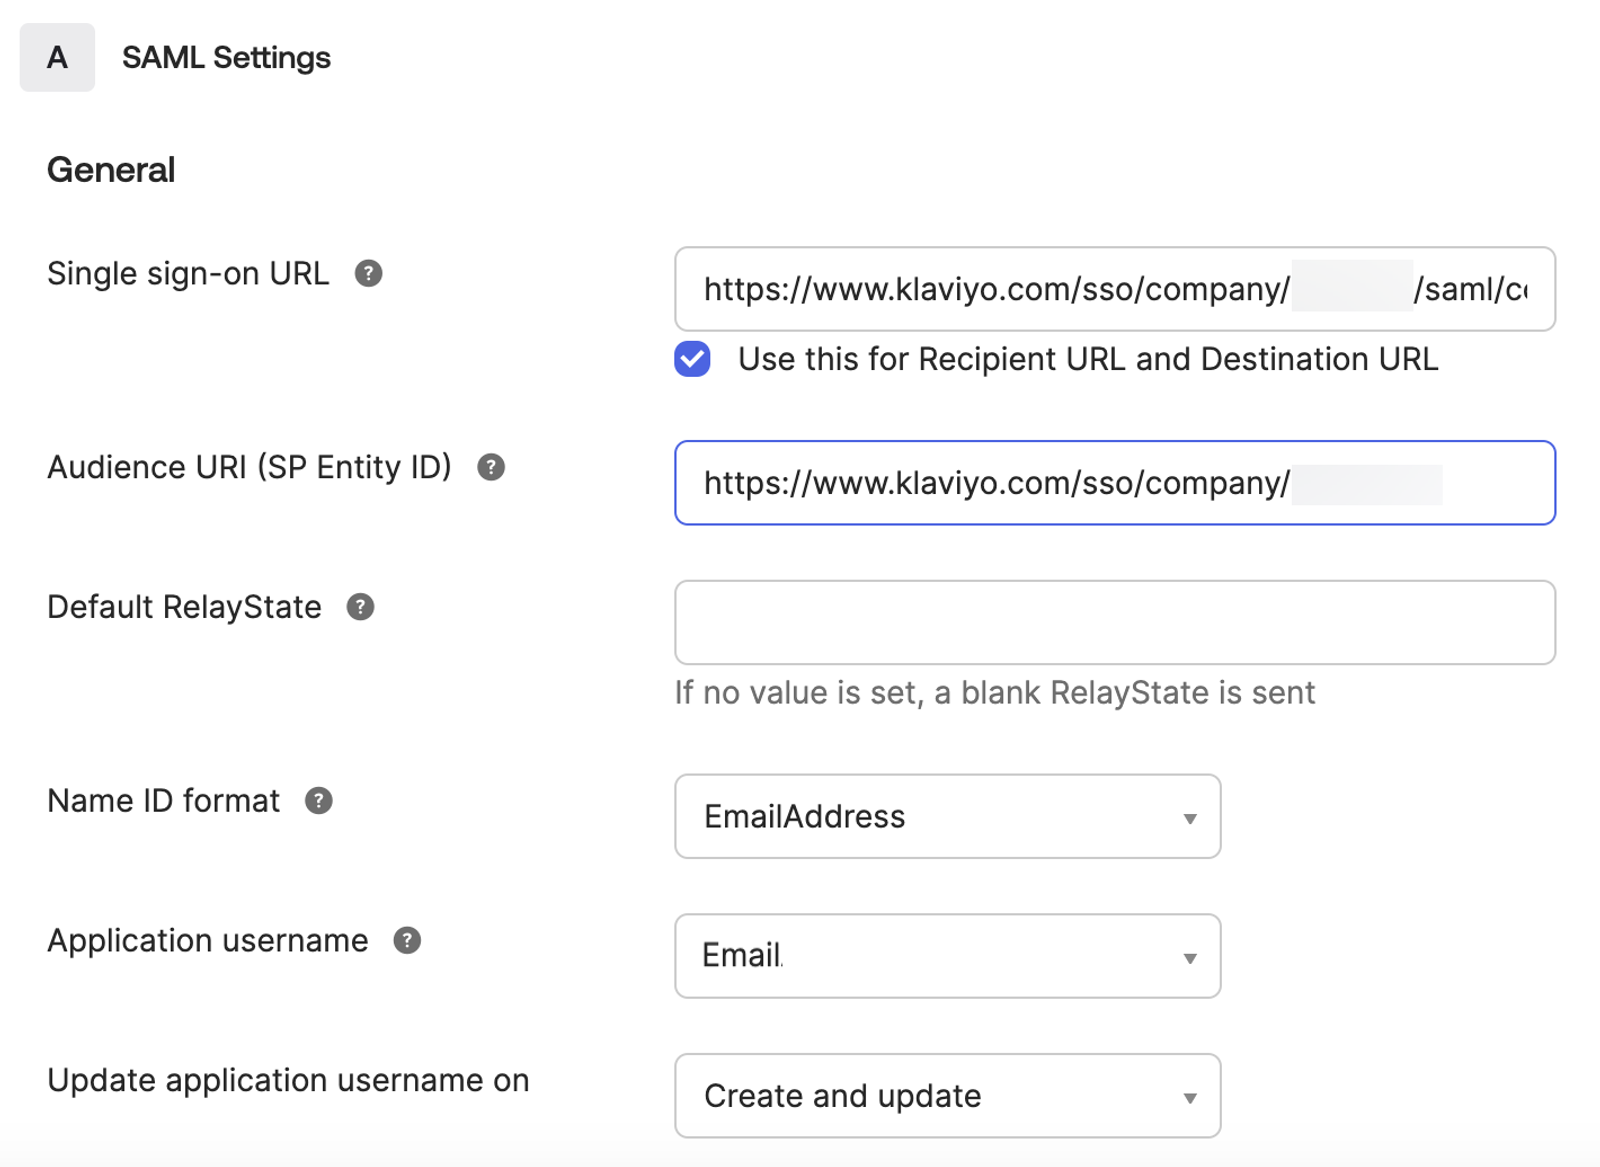
- In the Single sign-on URL field, paste in the Klaviyo SSO URL from the Klaviyo SSO setup screen.
- In the Audience URI (SP Entity ID) field, paste the Audience URI (Service Provider Entity ID) from Klaviyo.
- Set the Name ID format field to EmailAddress.
- Change the Application username to Email.
- Check that the Update application username on is set to Create and update.
- Click Next.
- Select I’m an Okta customer adding an internal app.
- Complete the remaining feedback options for your app as described in Okta’s setup guide.
- Scroll to the bottom of the page and click Finish.
- Go to the Sign On tab.
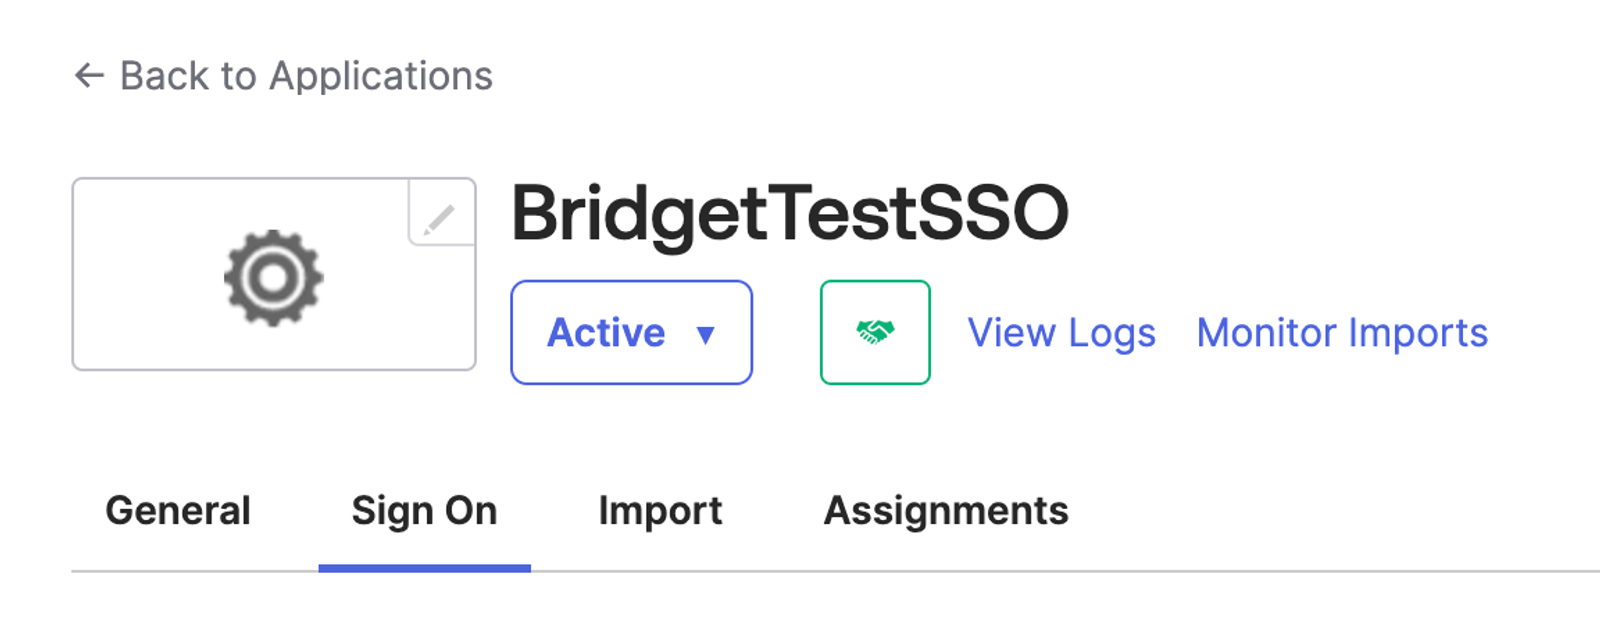
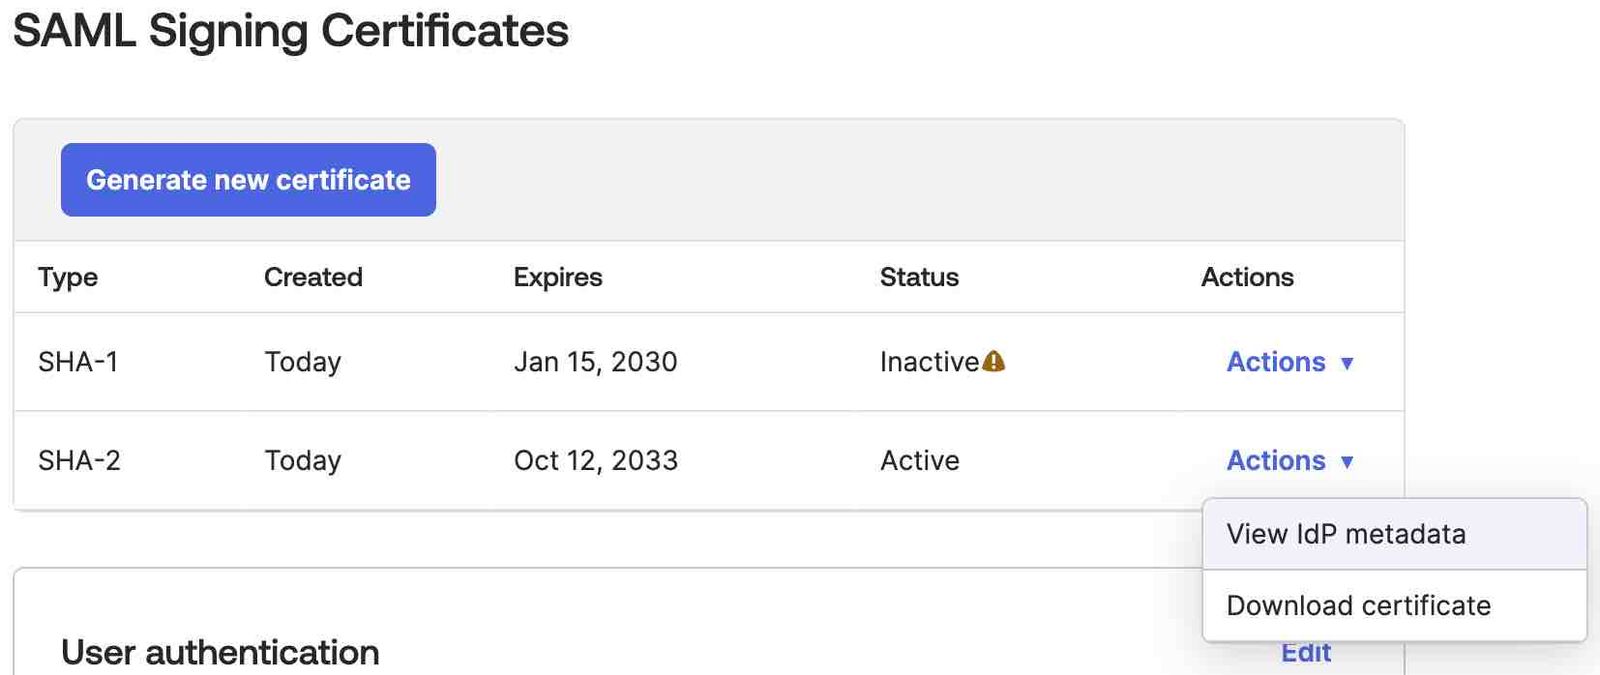
- Scroll down to the SAML Signing Certificates section.
- Find an active certificate and then click the Actions dropdown.
- Click View IdP metadata.
- A new tab will open that should look like the one below.
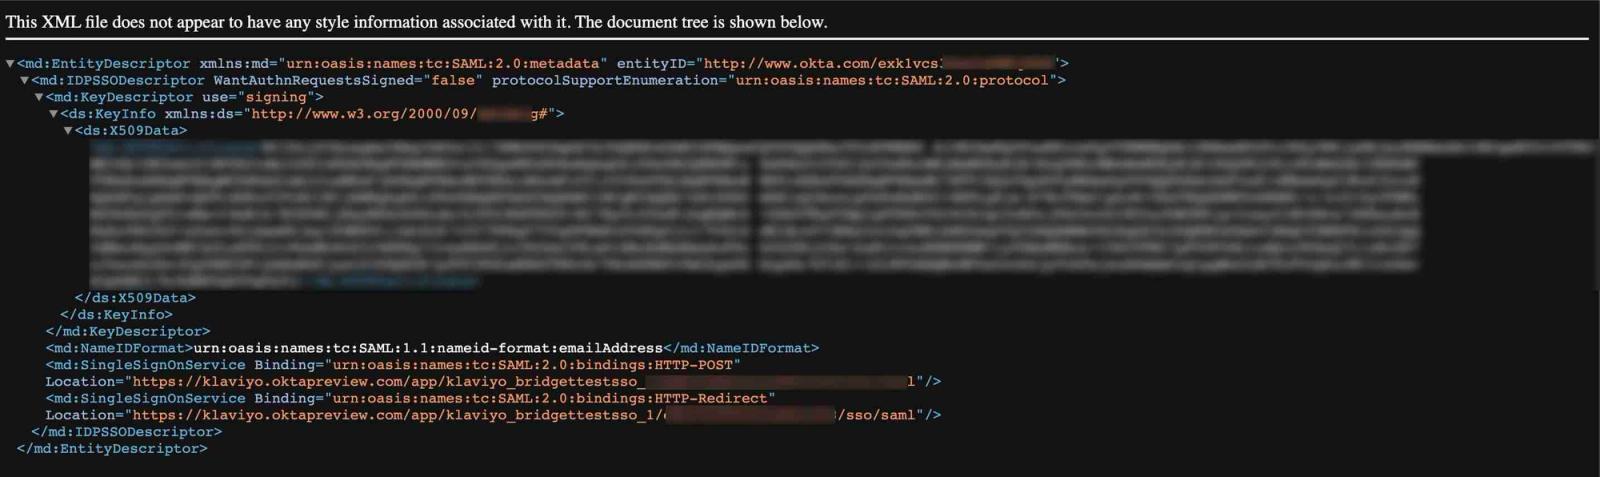
- In the new tab, right click and select Save as > Save so that you can upload this file to Klaviyo later.
- Navigate back to Okta.
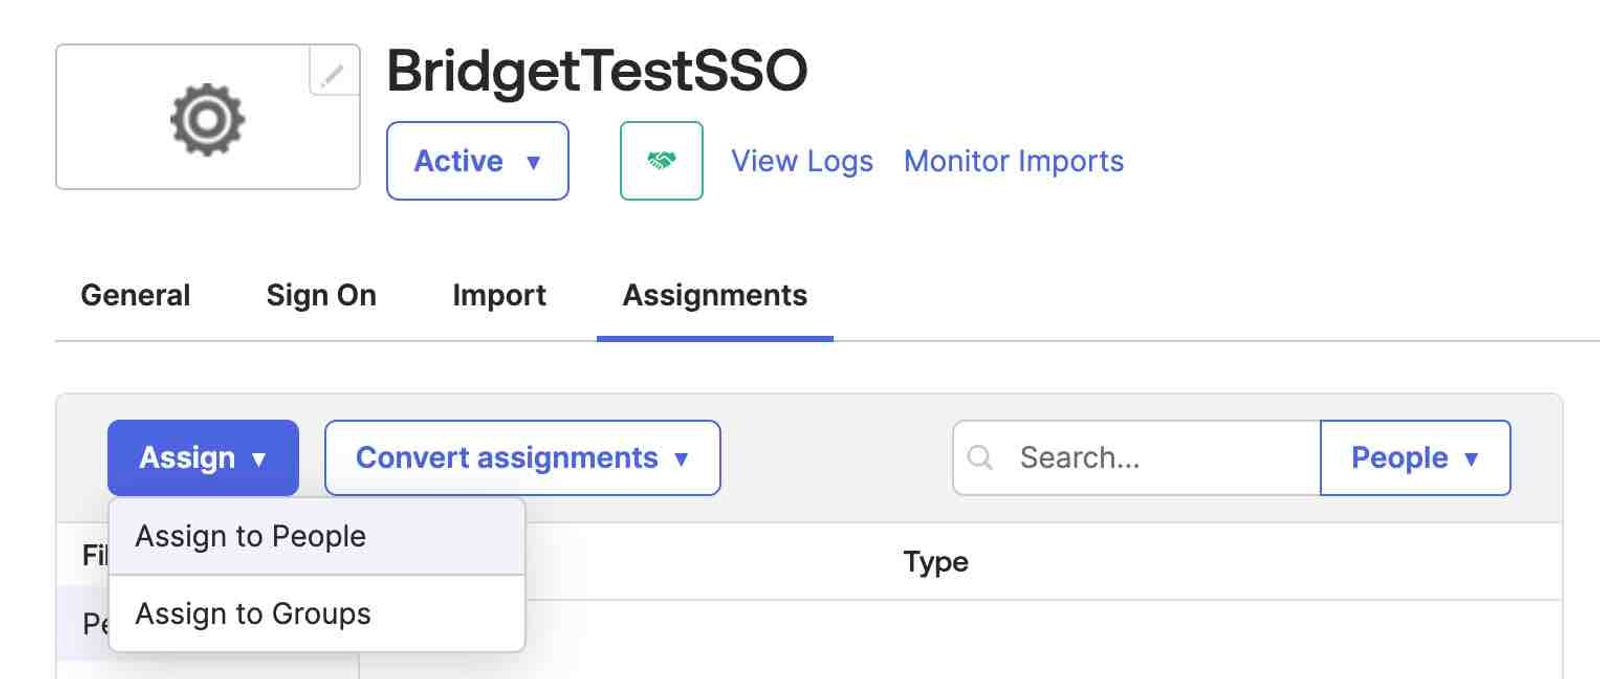
- Go to the Assignments tab.
- Click Assign.
- Choose whether to assign the app to an individual (i.e., people) or to a group.
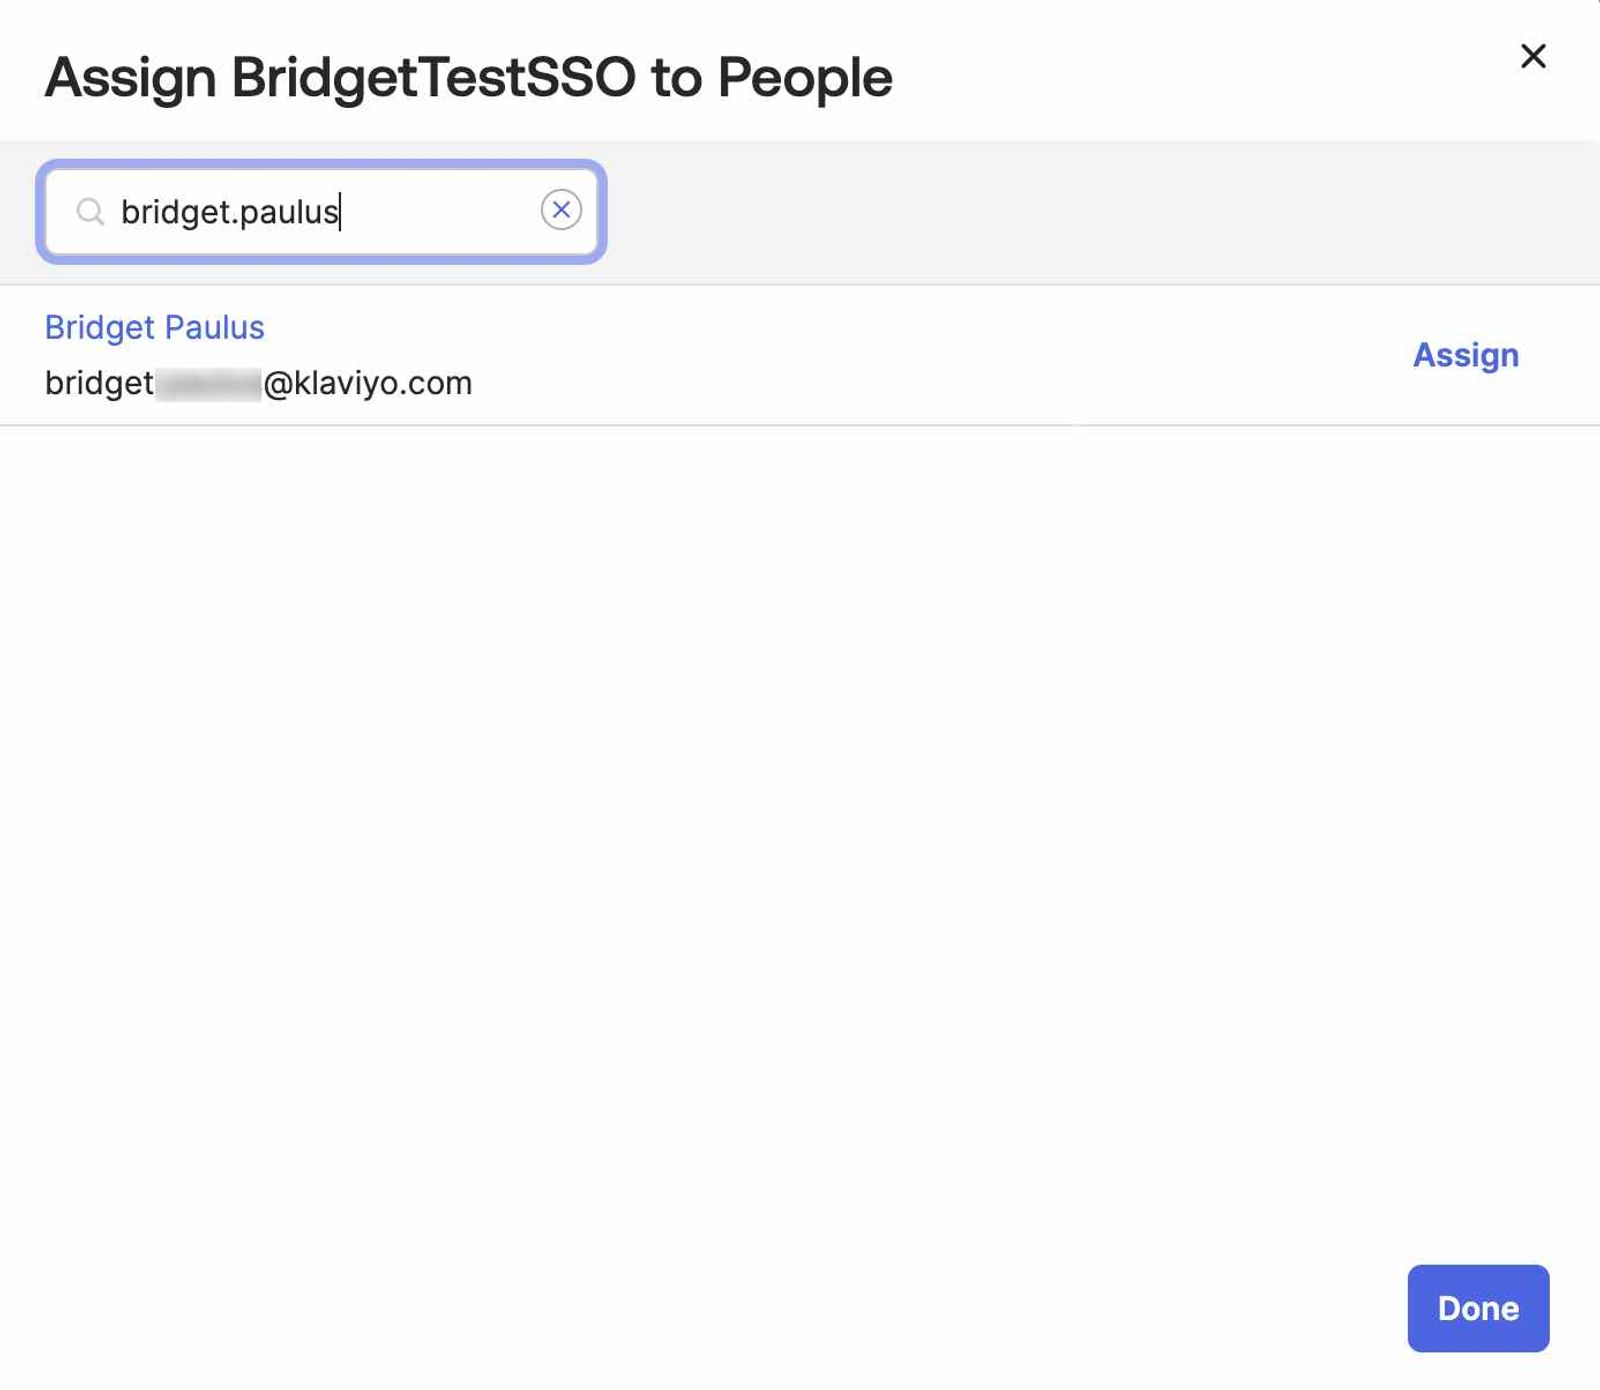
- Find the people or groups you want to assign Klaviyo to, and click Assign next to their name(s).
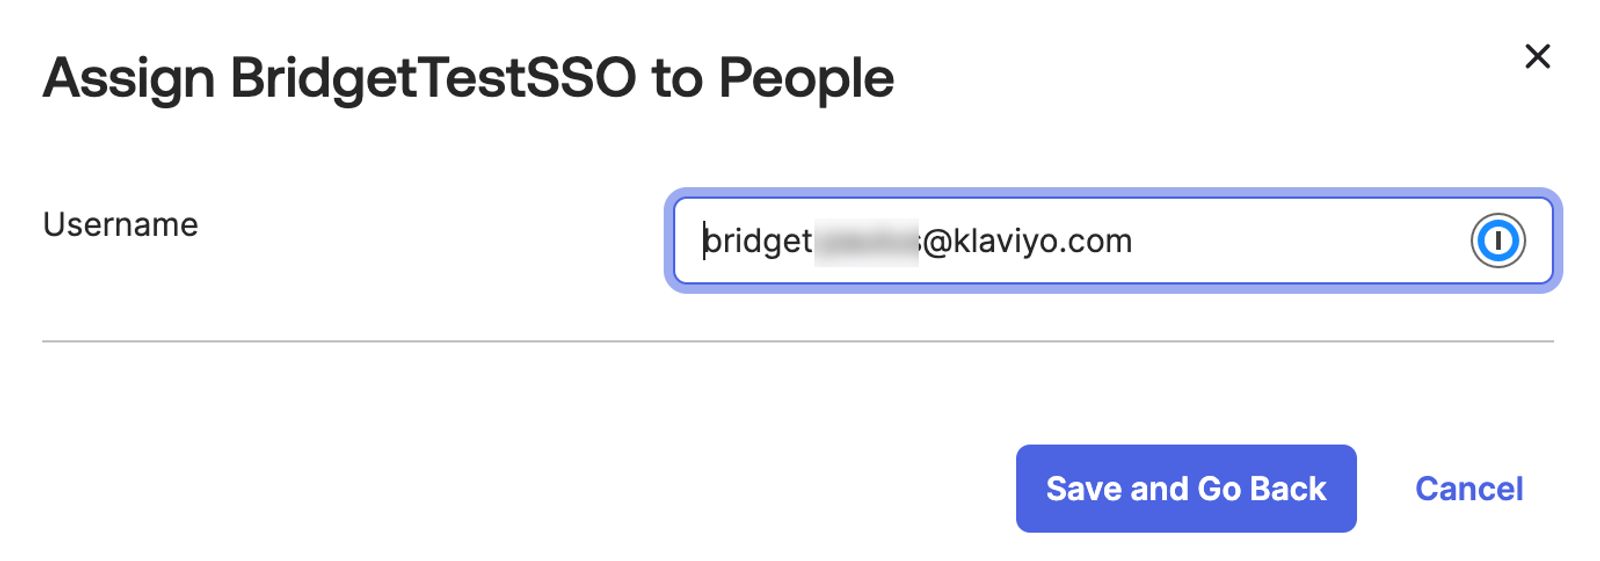
- If you’re selecting individuals:
- Choose the username for each individual; the default is their username in Okta.
- Click Save and go back.
- When you are finished, click Done.
One Login
- Log in to your One Login account.
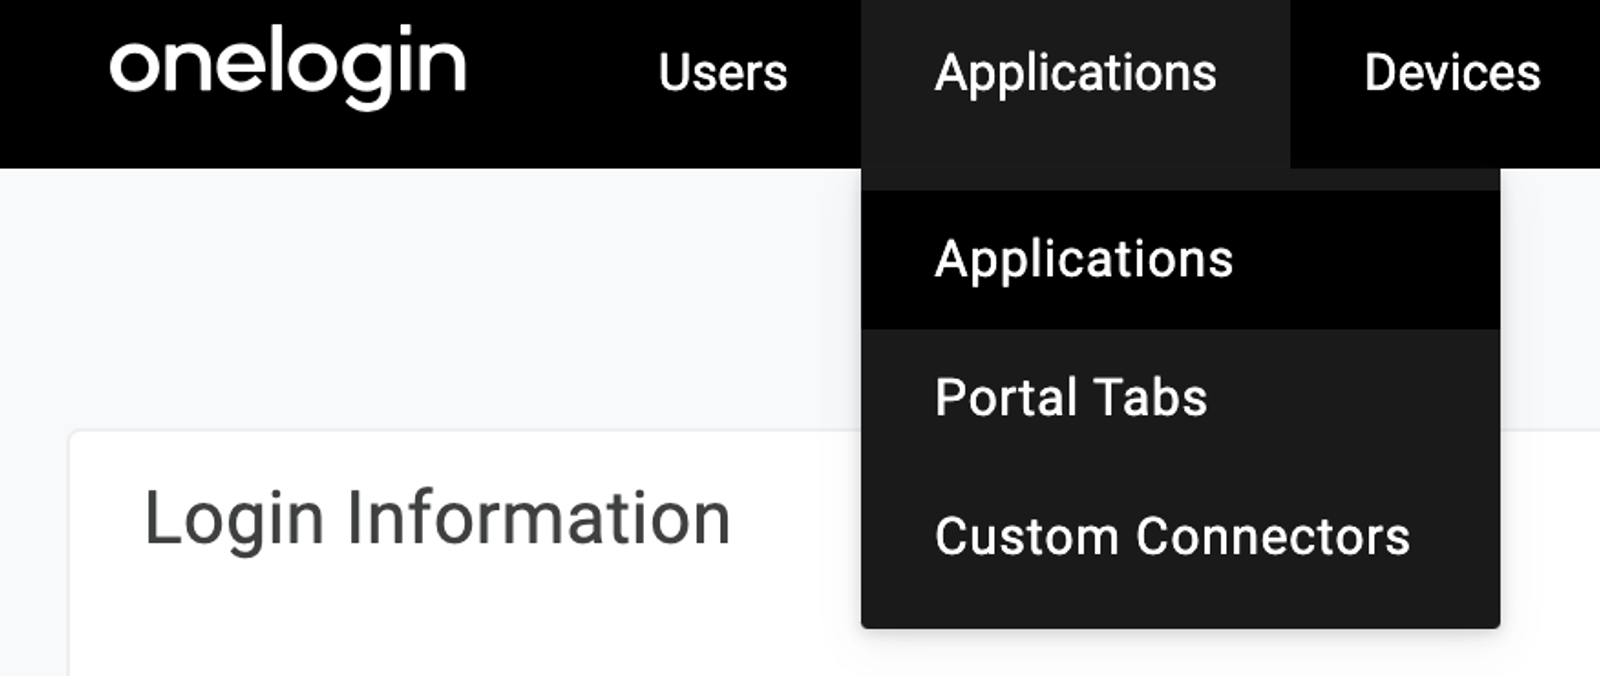
- Navigate to Applications > Applications.
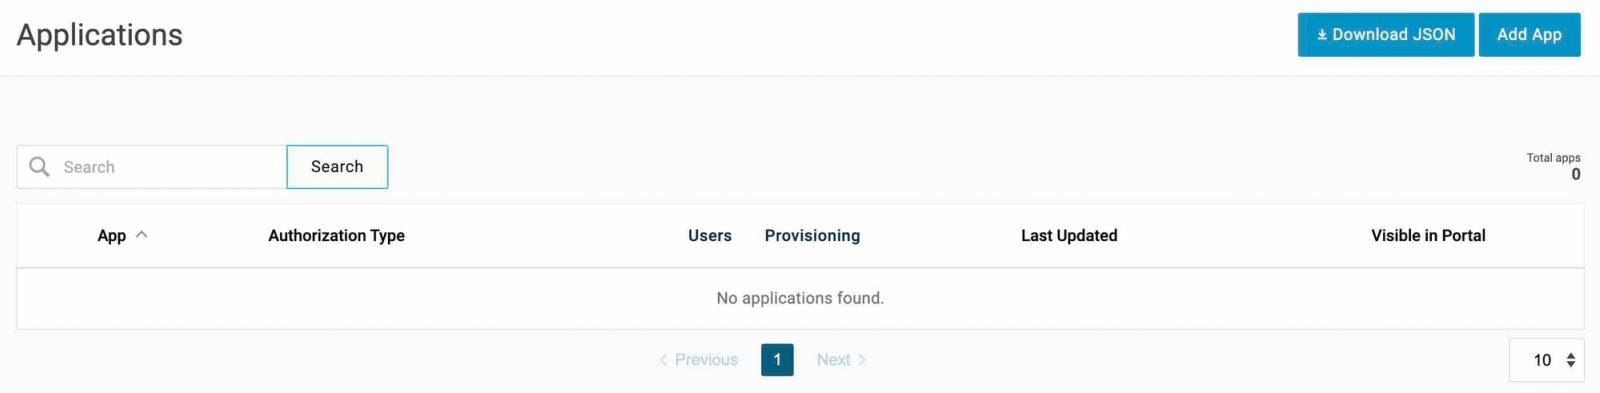
- Click Add App in the upper right corner.
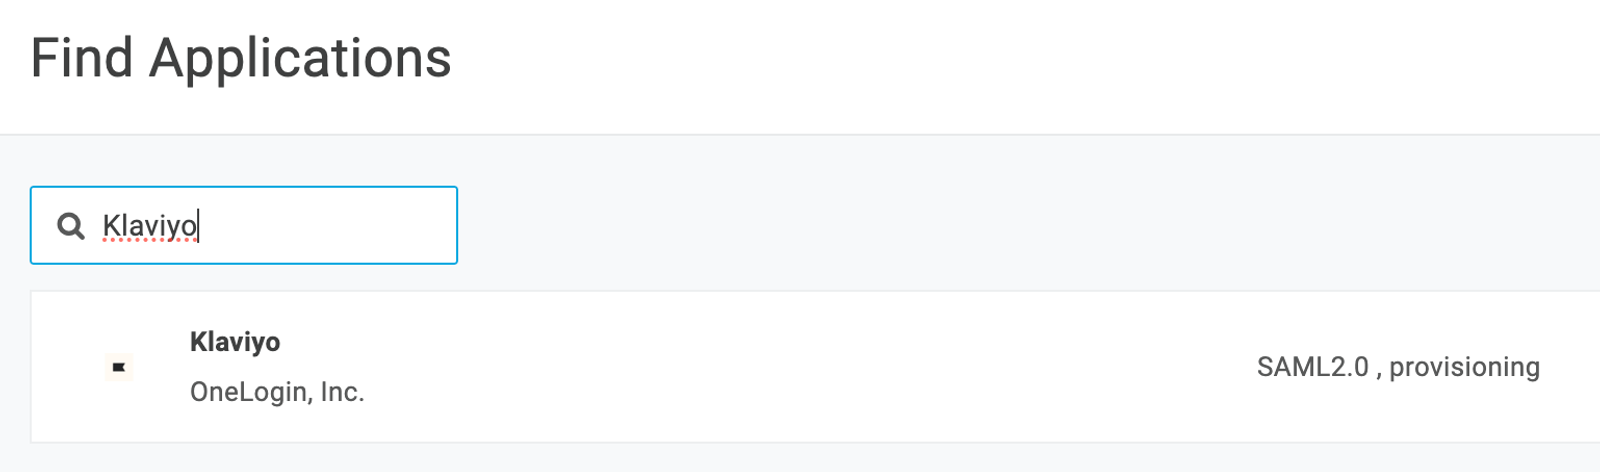
- Search for “Klaviyo” and then select the result that appears.
- Optional: choose the display name, upload a new icon, or add a description for this app.
- Click Save in the upper right.
- Navigate to Configuration in the left sidebar.
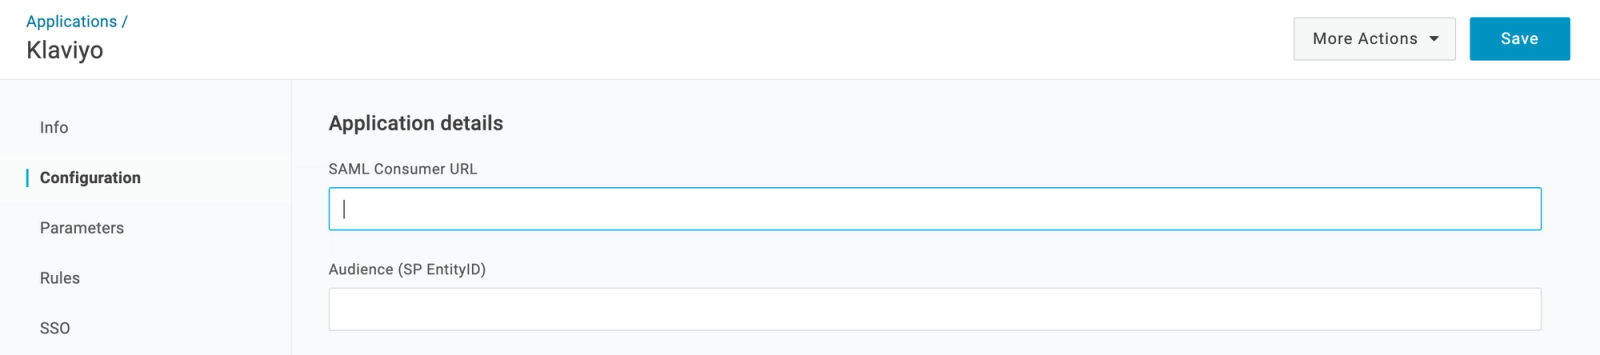
- In the SAML Consumer URL field, paste your Klaviyo SSO URL.
- In the Audience (SP EntityID) field, paste your Audience URI (Service Provider Entity ID).
- Click Save.
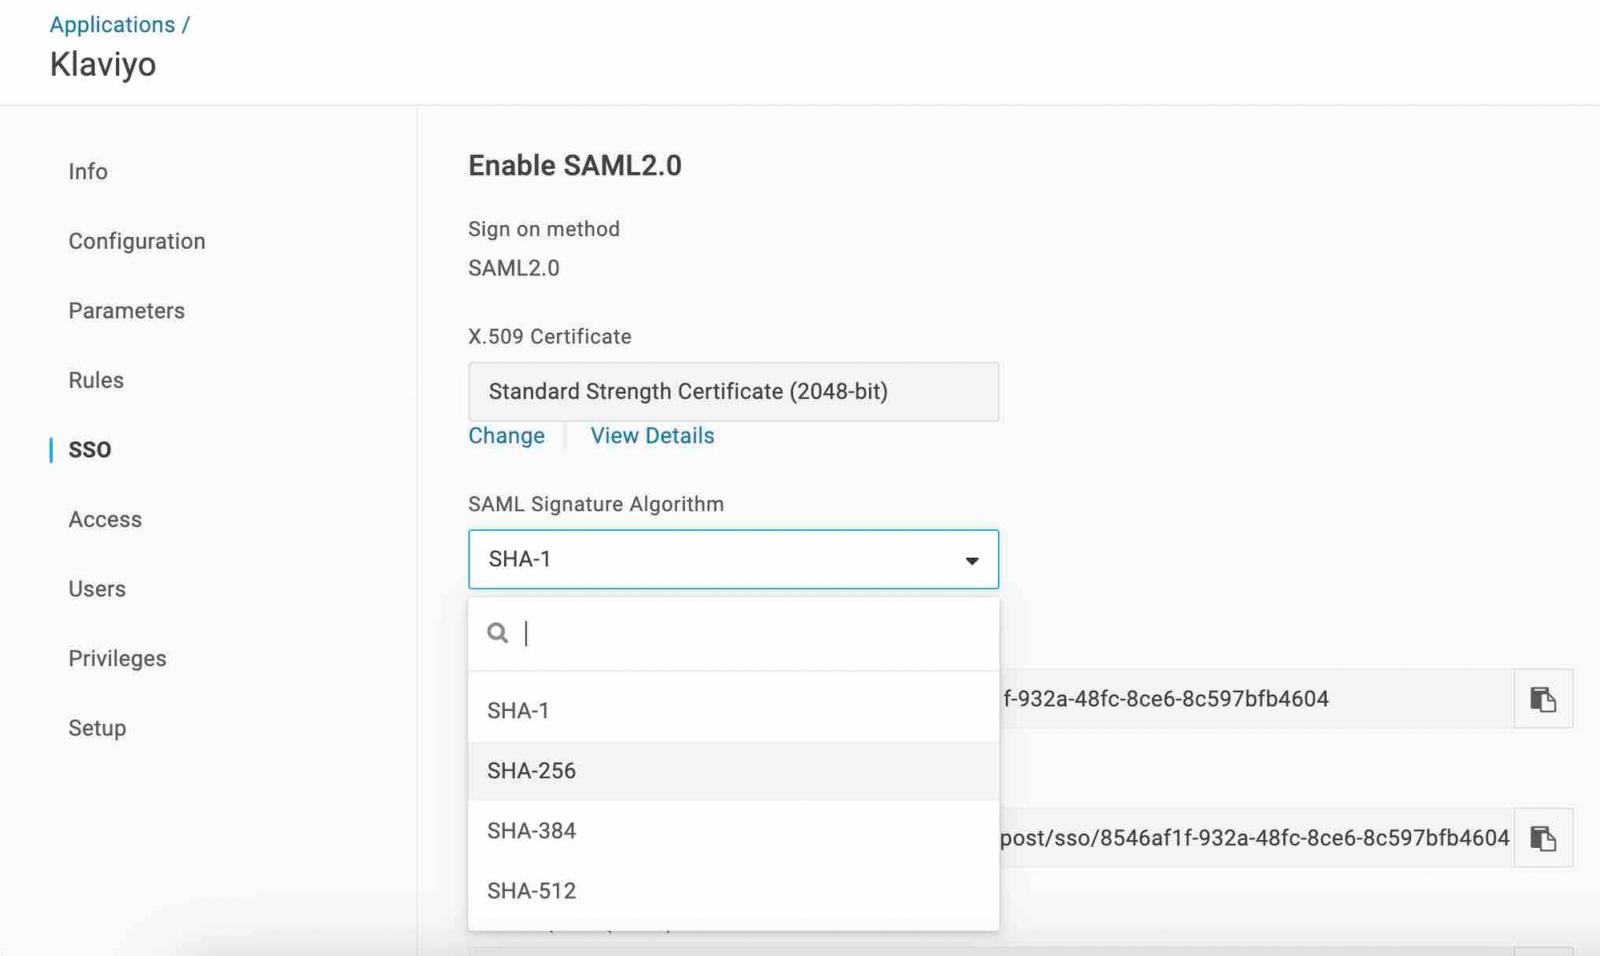
- Click SSO in the left sidebar.
- Open the SAML Signature Algorithm dropdown.
- Select SHA-256.
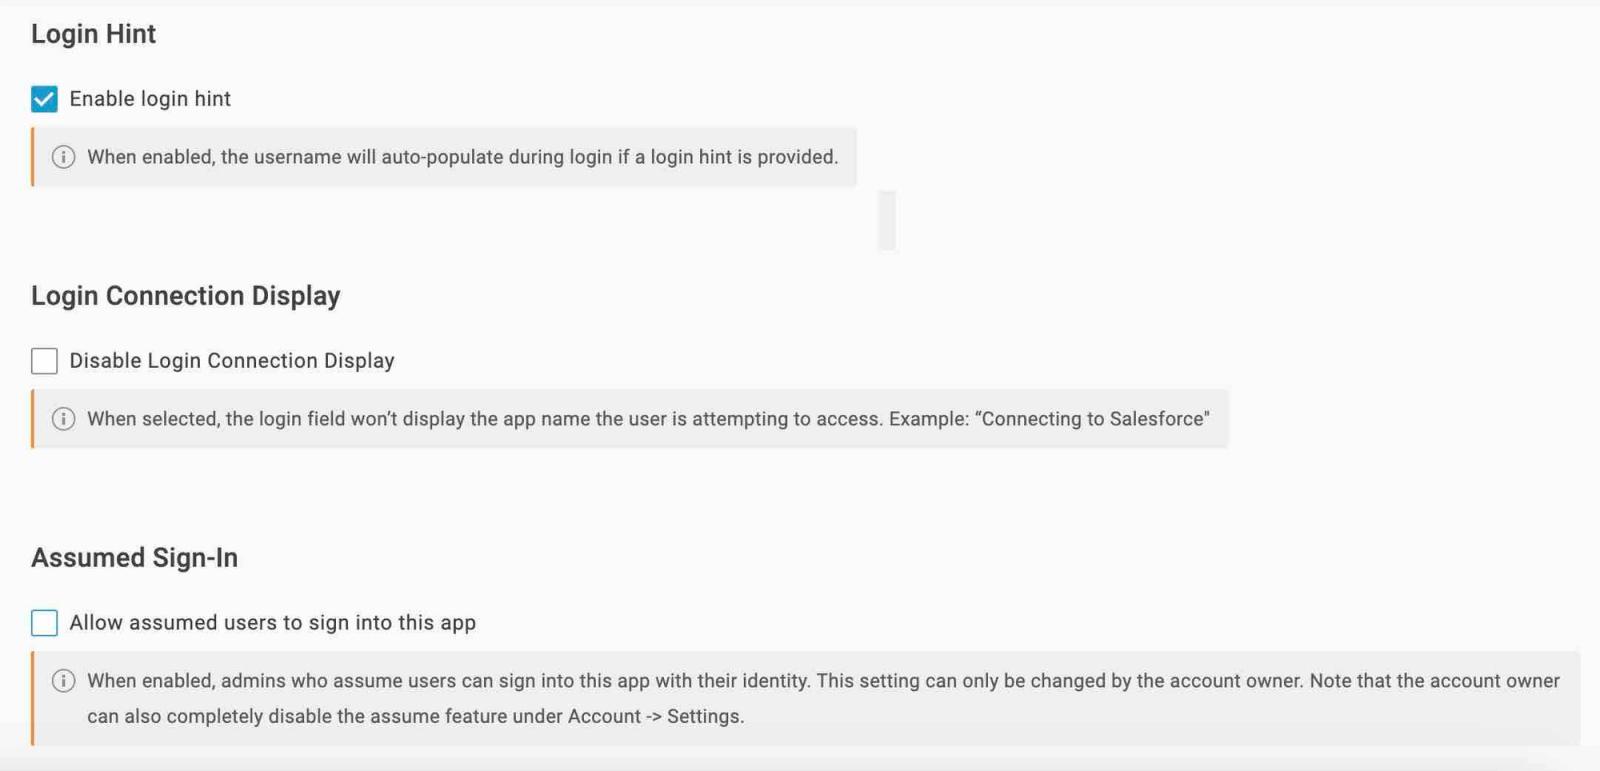
- Optional: scroll down to change your login display settings.
- Click Save.
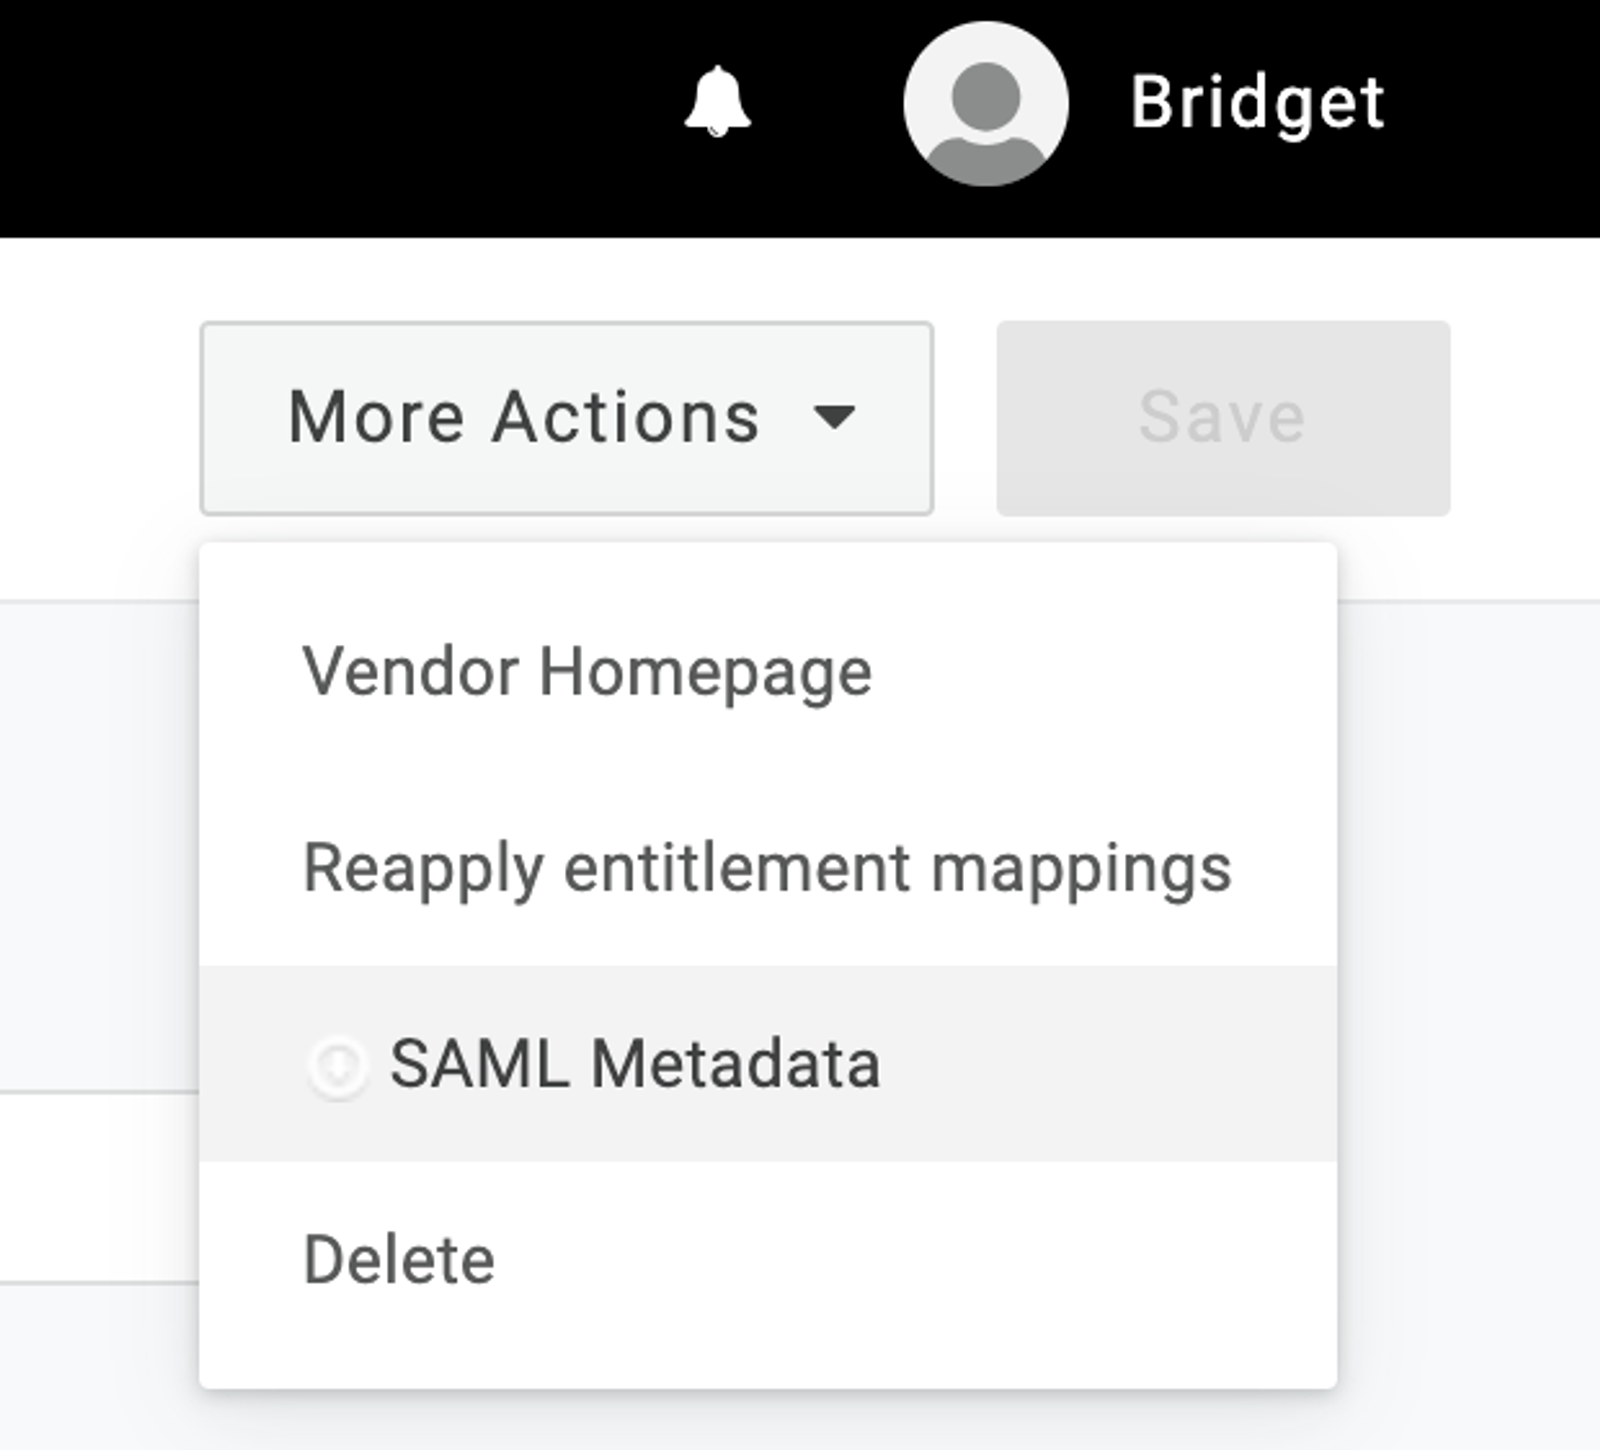
- Open the More Actions dropdown in the upper right.
- Select SAML Metadata. This will download the file you need to upload in the next section.
Before moving on to the next section, you need to add users to the Klaviyo app in One Login and then assign their roles.
- To add users to the Klaviyo app, click Users > Users in the upper left.
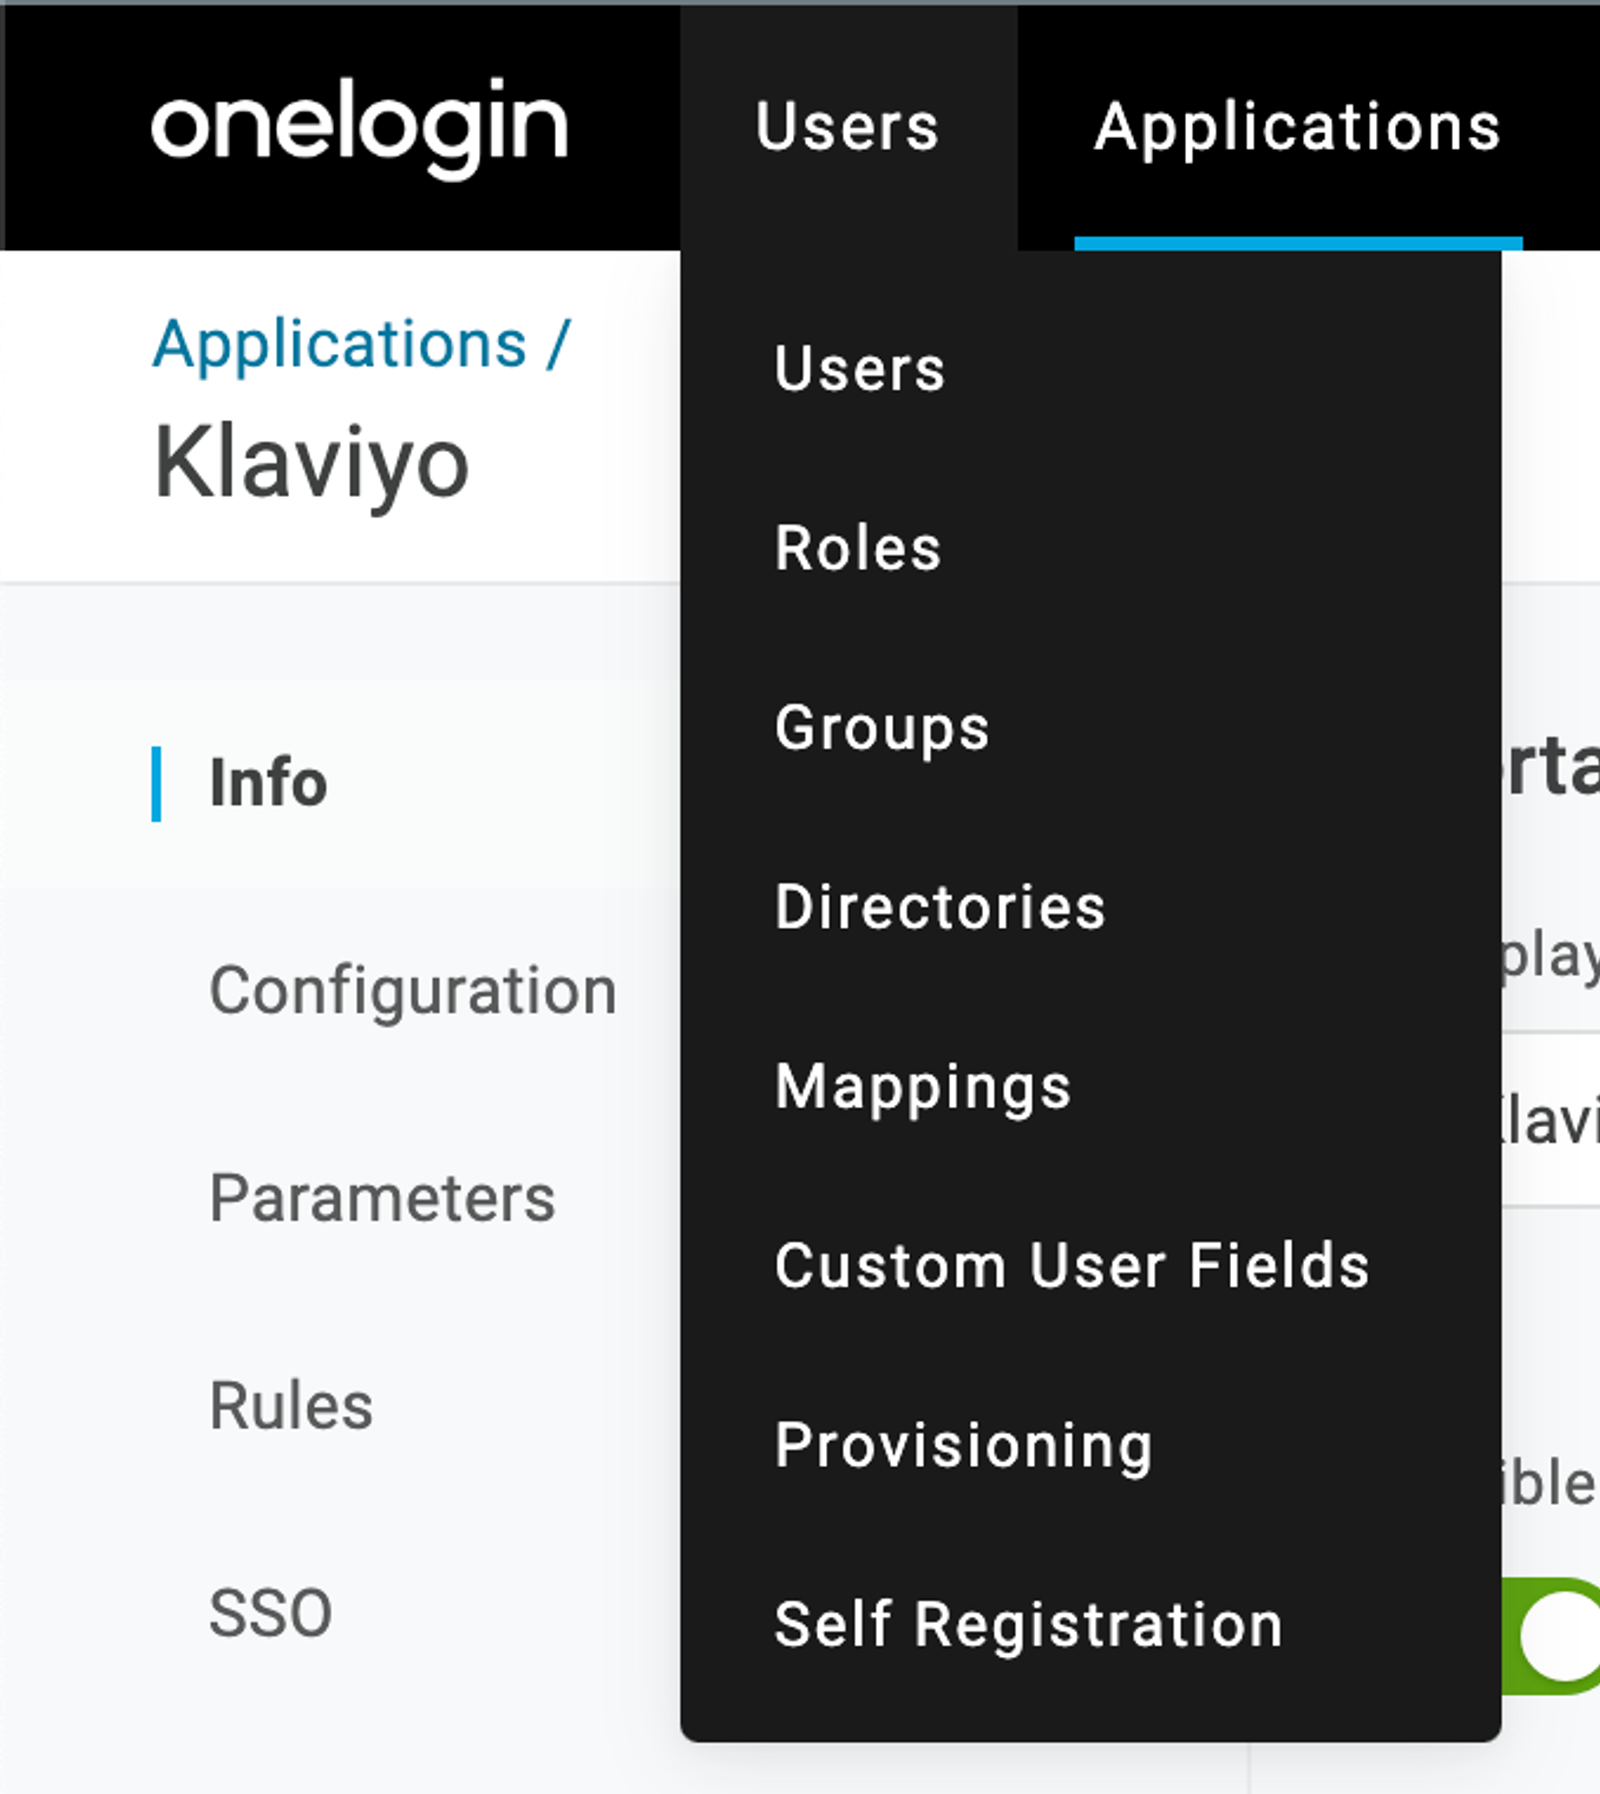
- Select a user to access Klaviyo. We recommend assigning the person who is setting up SSO in Klaviyo.
- Select Applications in the left sidebar.
- Click the plus button on the right side to add an application to this user.
- Select Klaviyo from the dropdown.
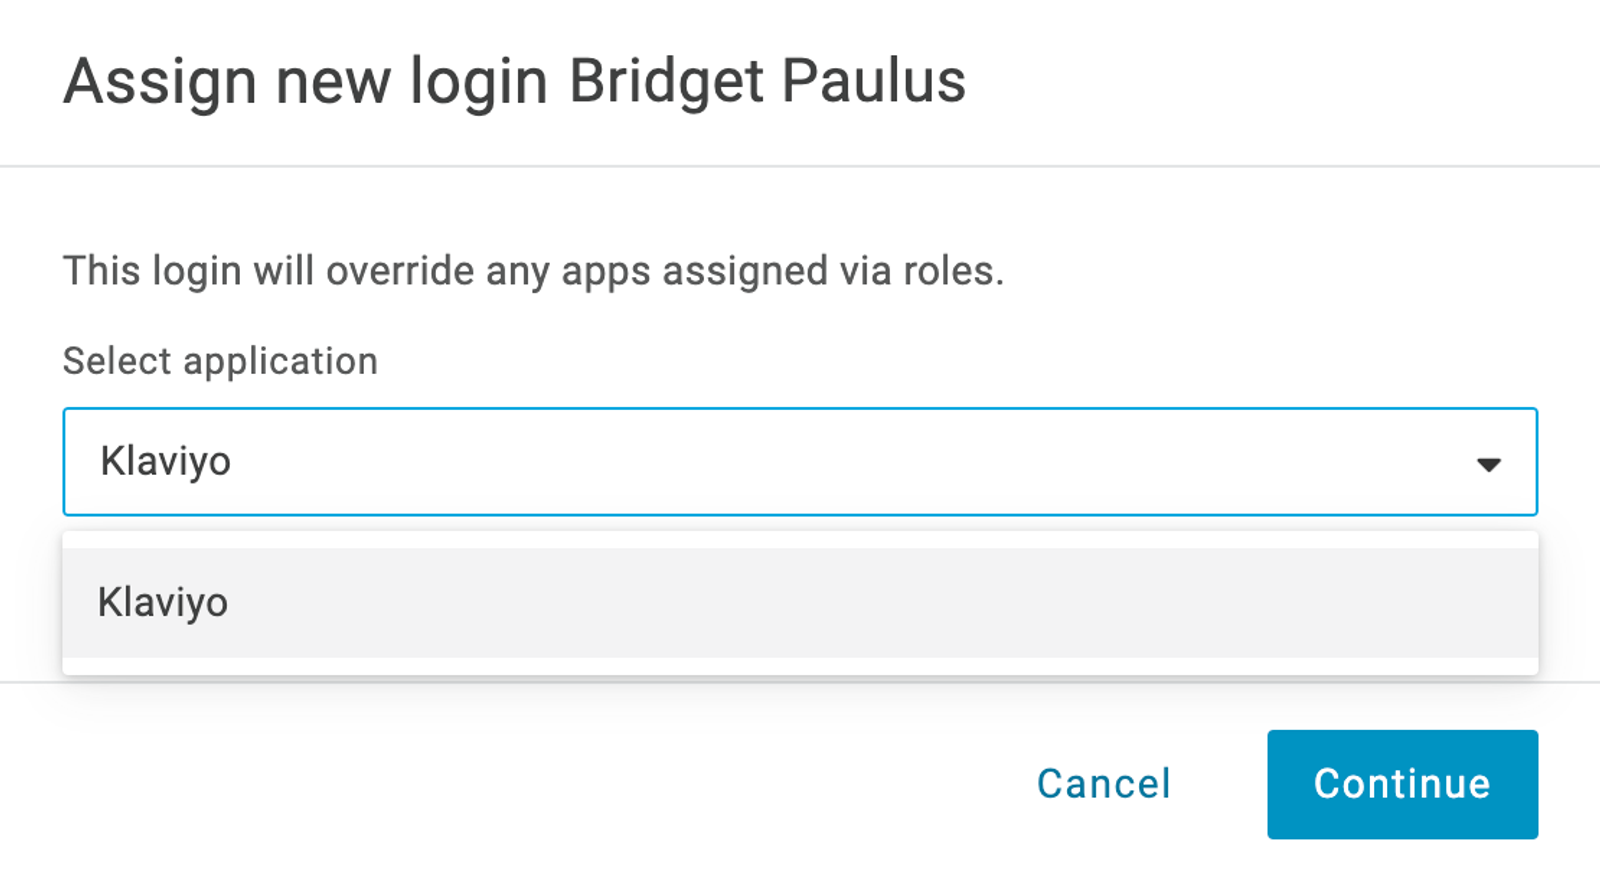
- Click Continue.
- In the resulting modal, scroll down to the role dropdown.
- Open this dropdown and select the Klaviyo role this user should be assigned.
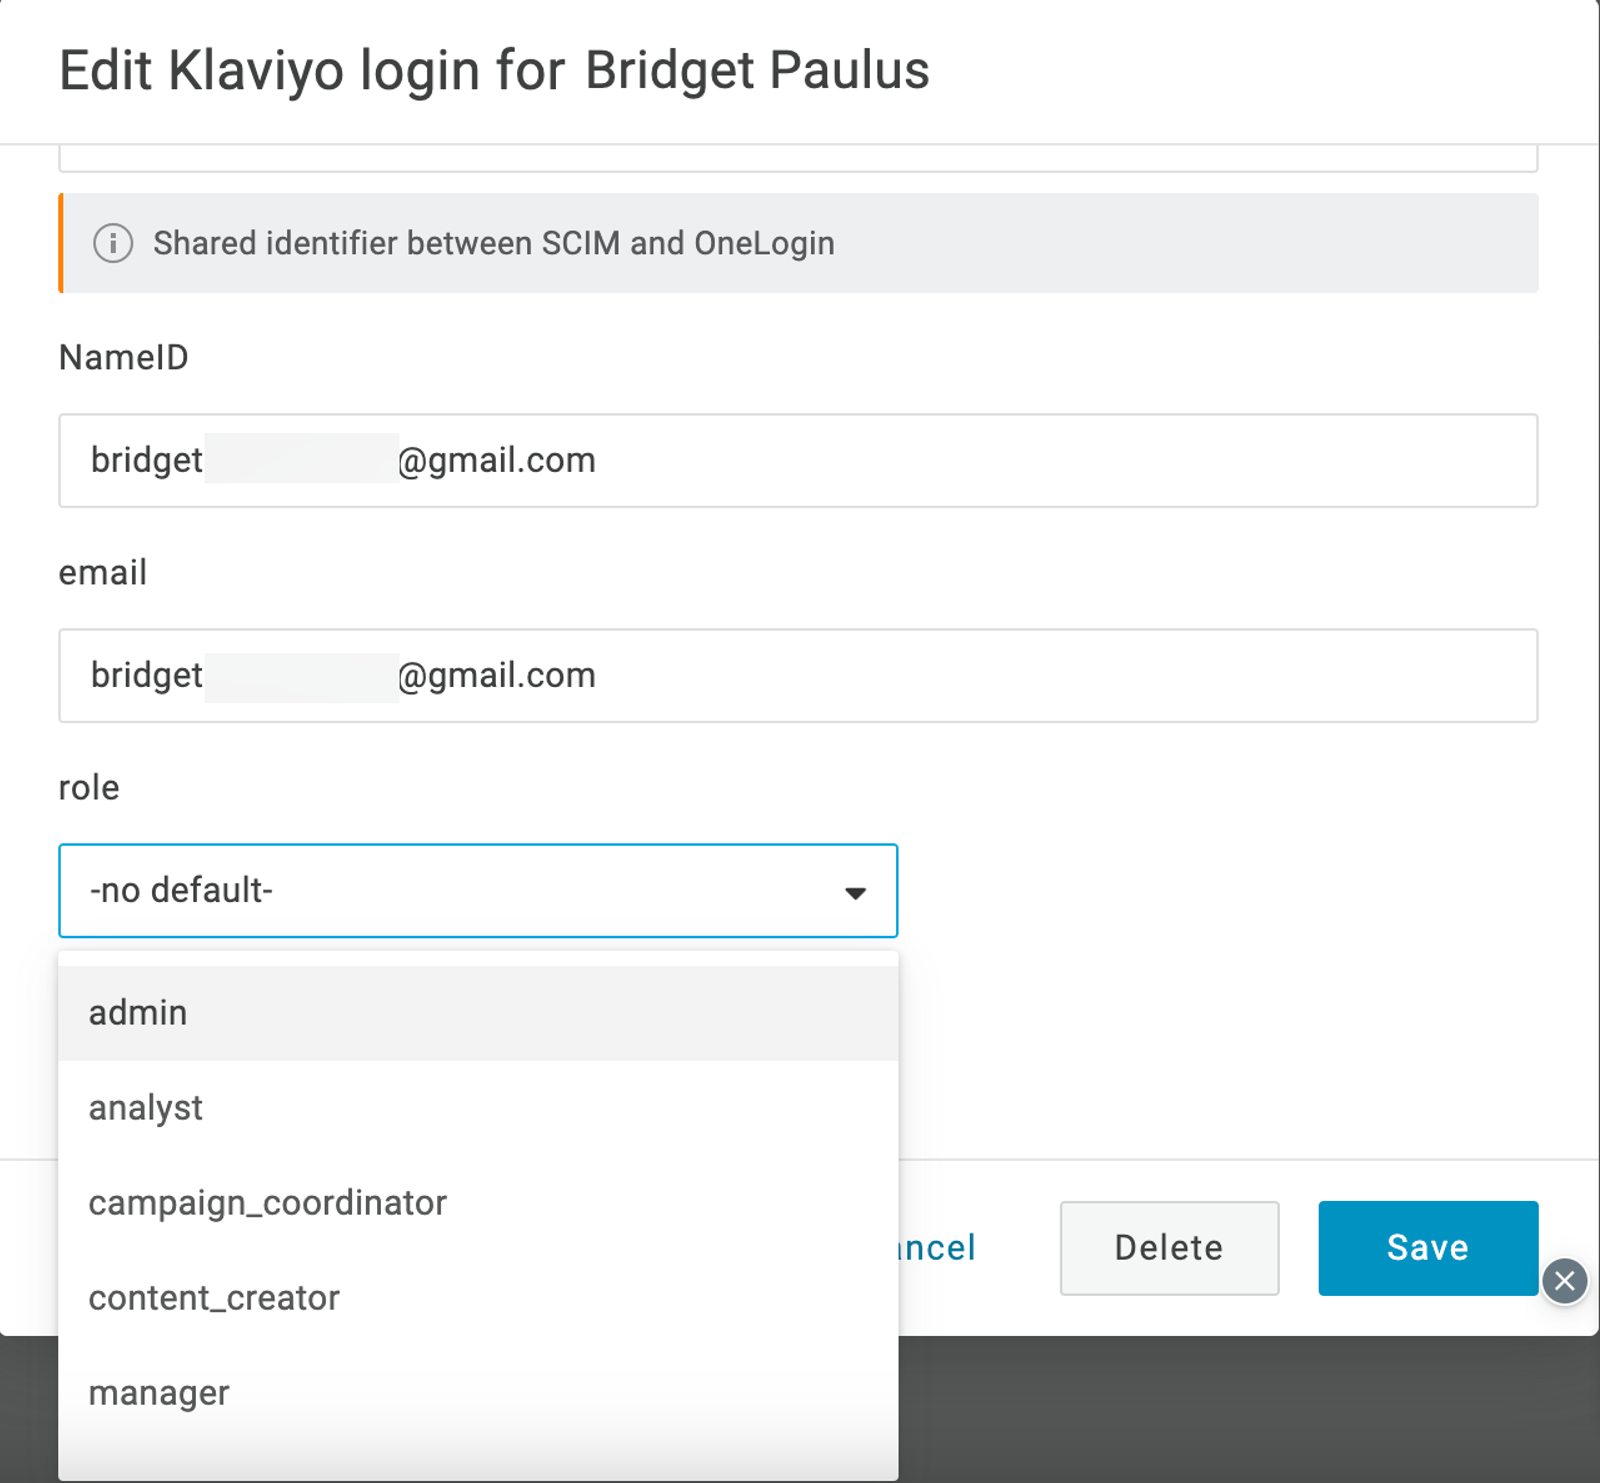
- Click Save.
Microsoft Entra ID (Azure AD)
- Log in to Microsoft Entra ID (formerly known as Azure AD).
- Click Microsoft Entra ID.
- Select the Add dropdown and then click Enterprise Application.
- Click Create your own application.
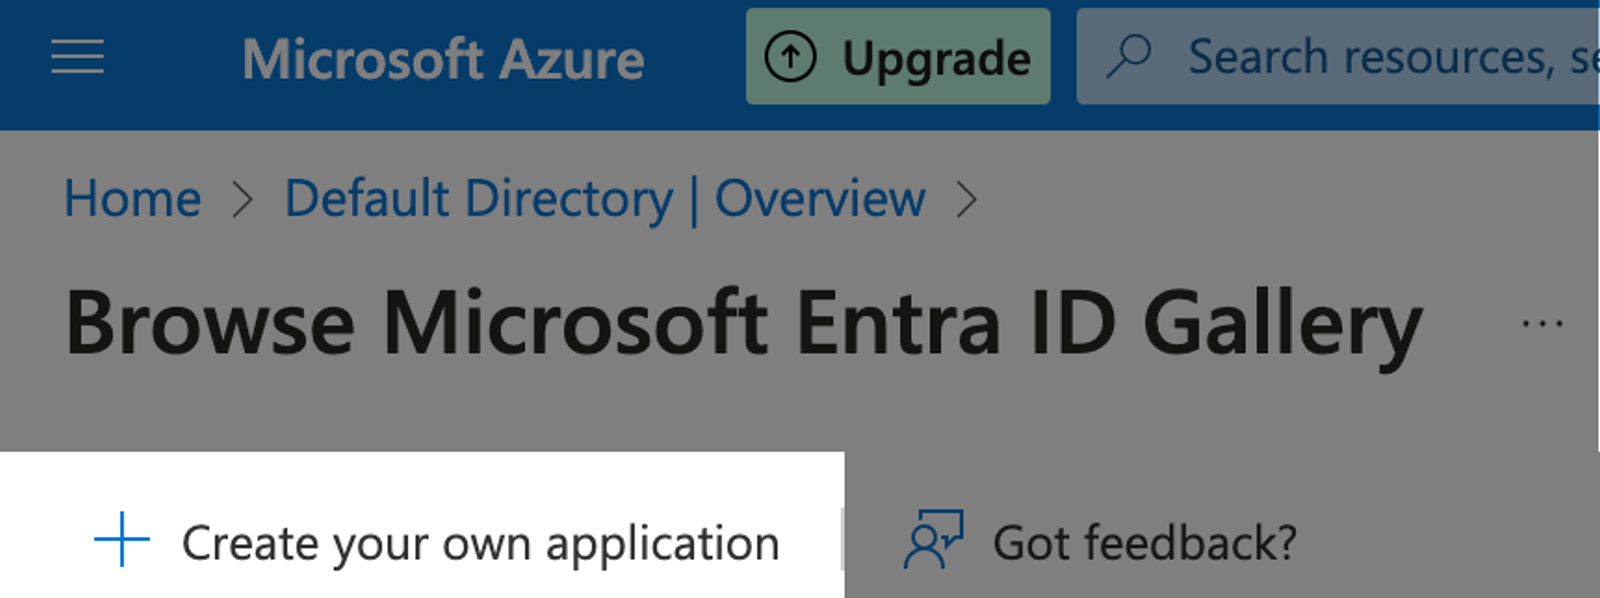
- Name the application “Klaviyo,” then click Create.
- Click Single sign-on in the left sidebar.
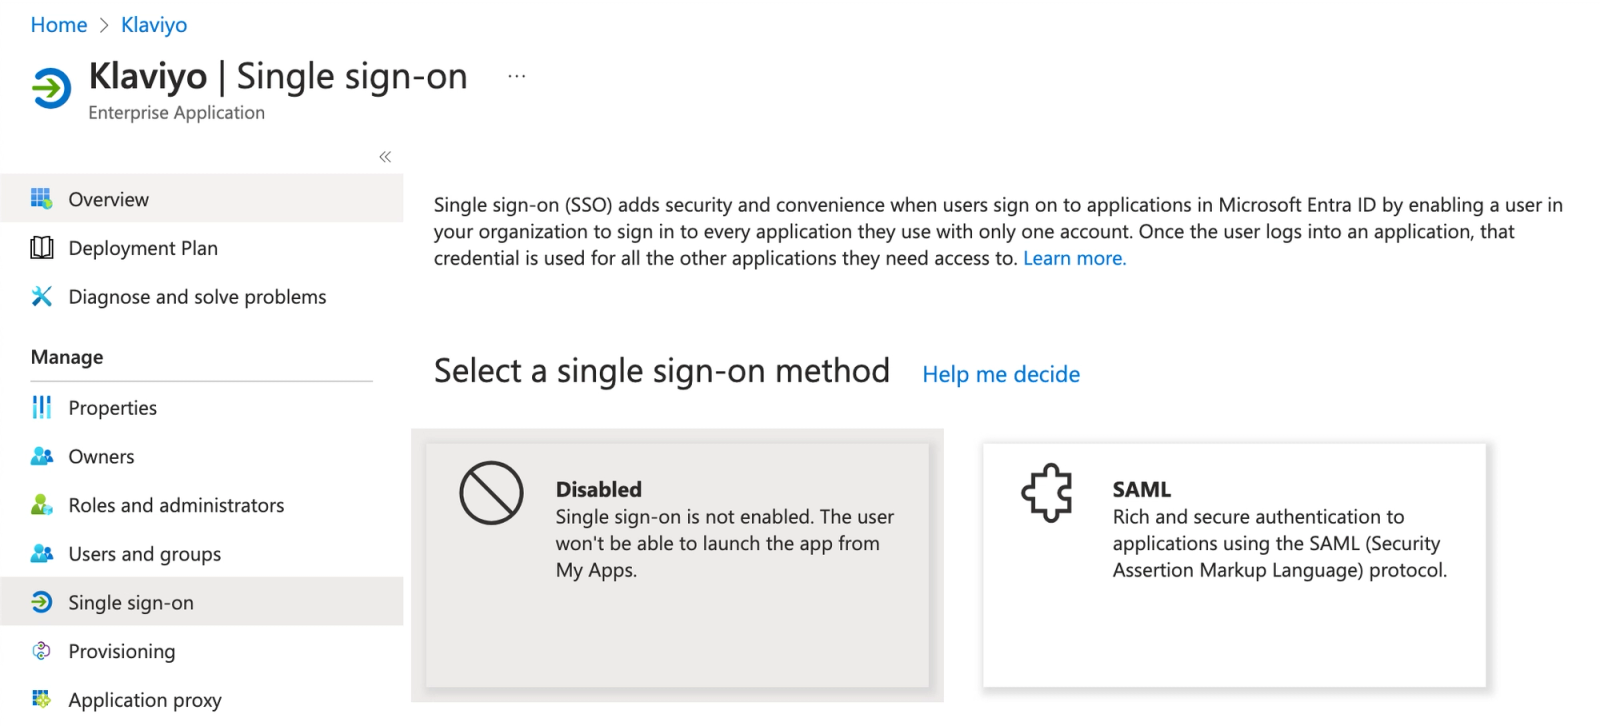
- Select SAML.
- Click Edit in the Basic SAML Configuration box.
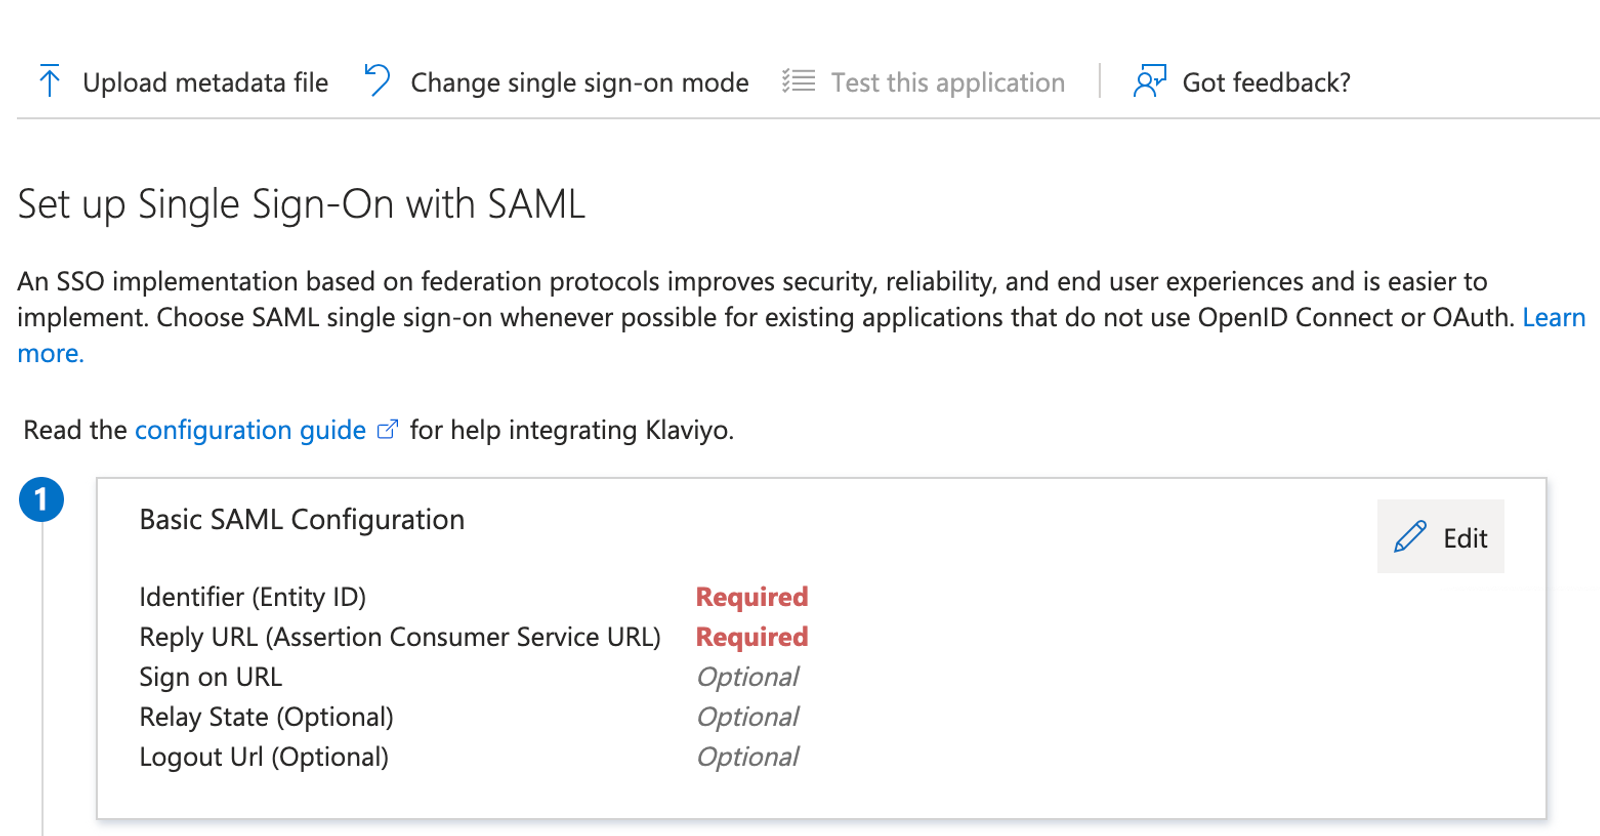
- In the right sidebar that appears, click Add identifier under Identifier (Entity ID).
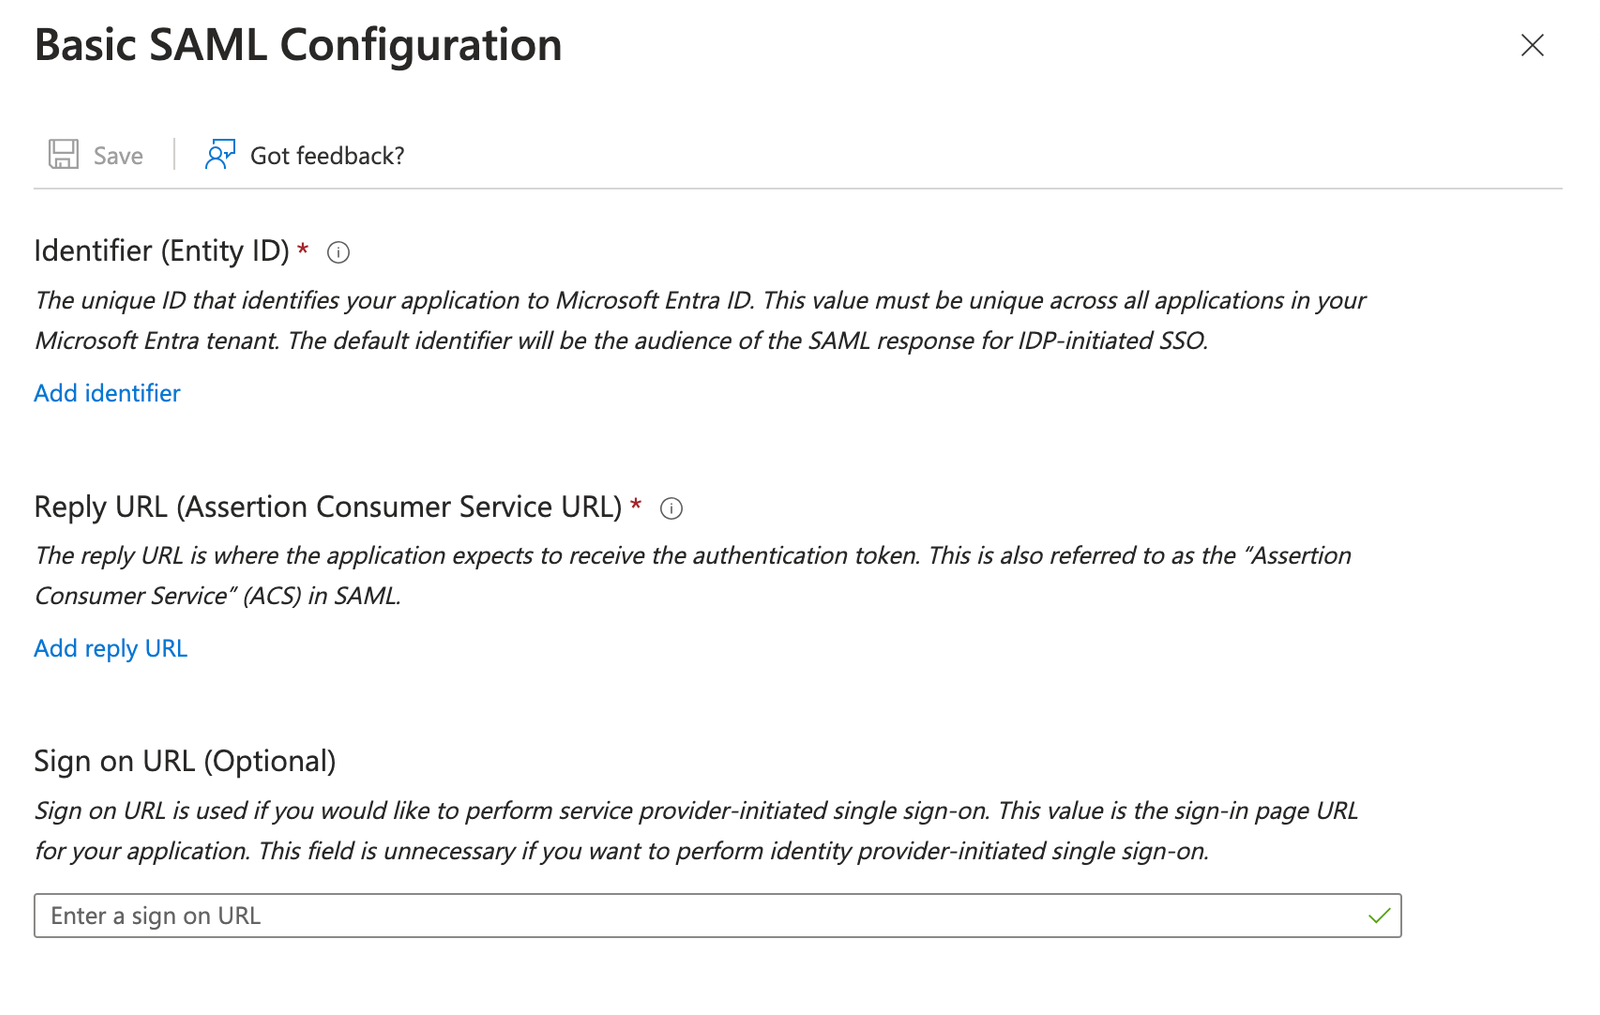
- In the field that appears, paste in the Audience URI (Service Provider Entity ID) from Klaviyo.
- Under Reply URL (Assertion Consumer Service URL), click Add reply URL.
- Here, paste the Klaviyo SSO URL from Klaviyo.
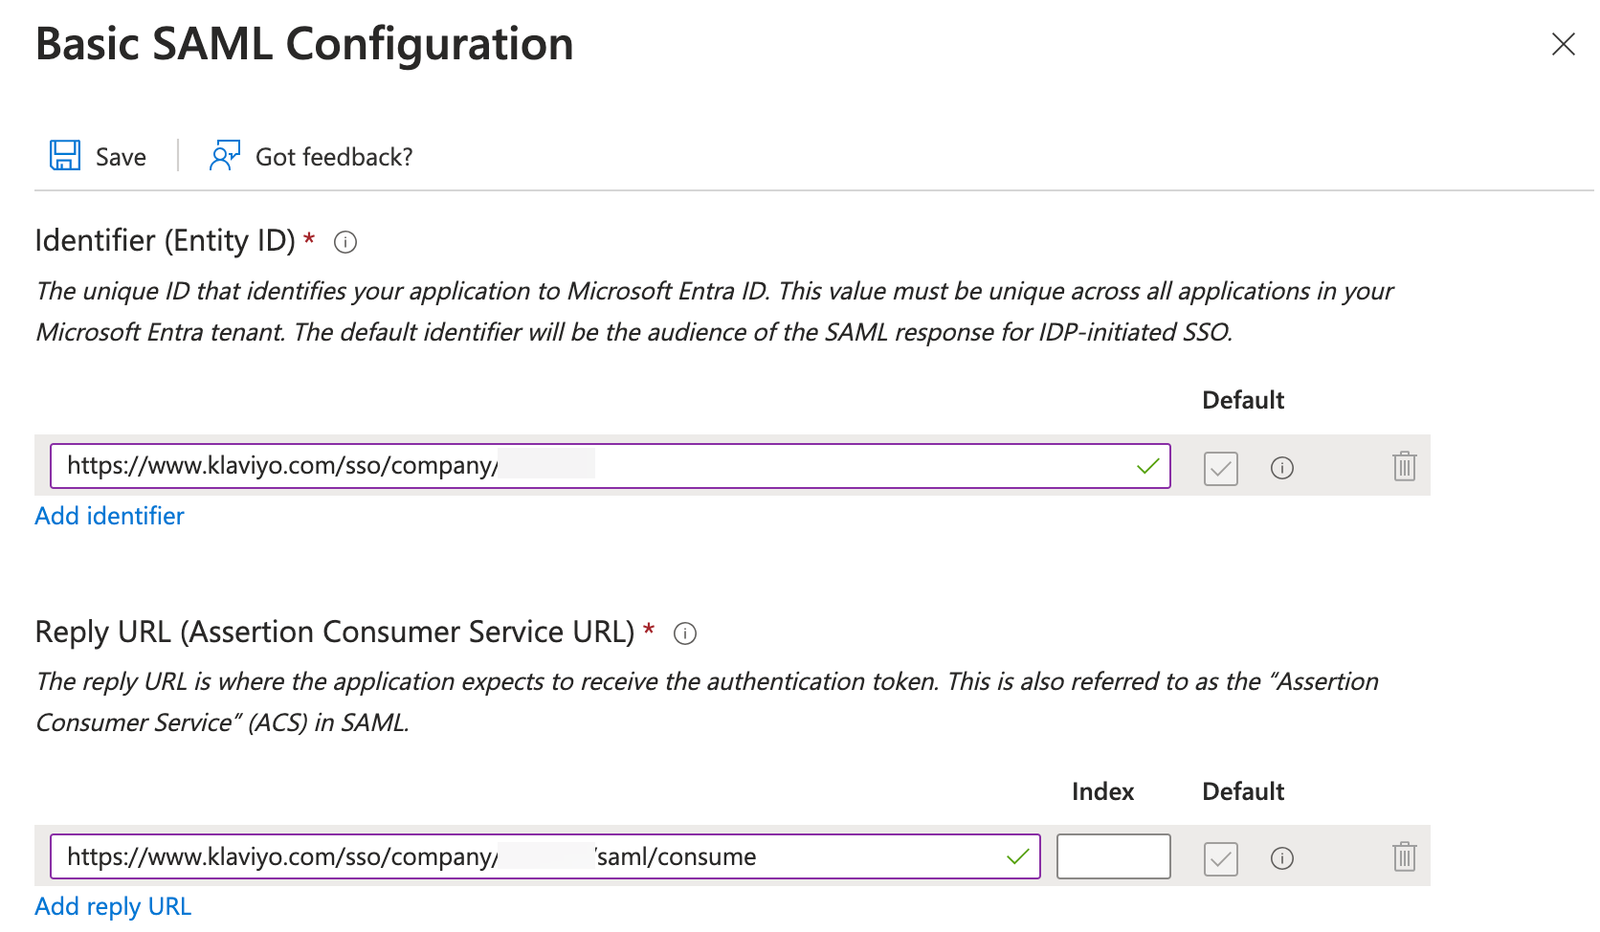
- Note: if you want to add in a Sign on URL, you must first create a workplace ID, which is discussed in the next section. We recommend finishing the setup process and then coming back to this step.
- Click Save in the top left corner of the sidebar before clicking the X in the upper right.
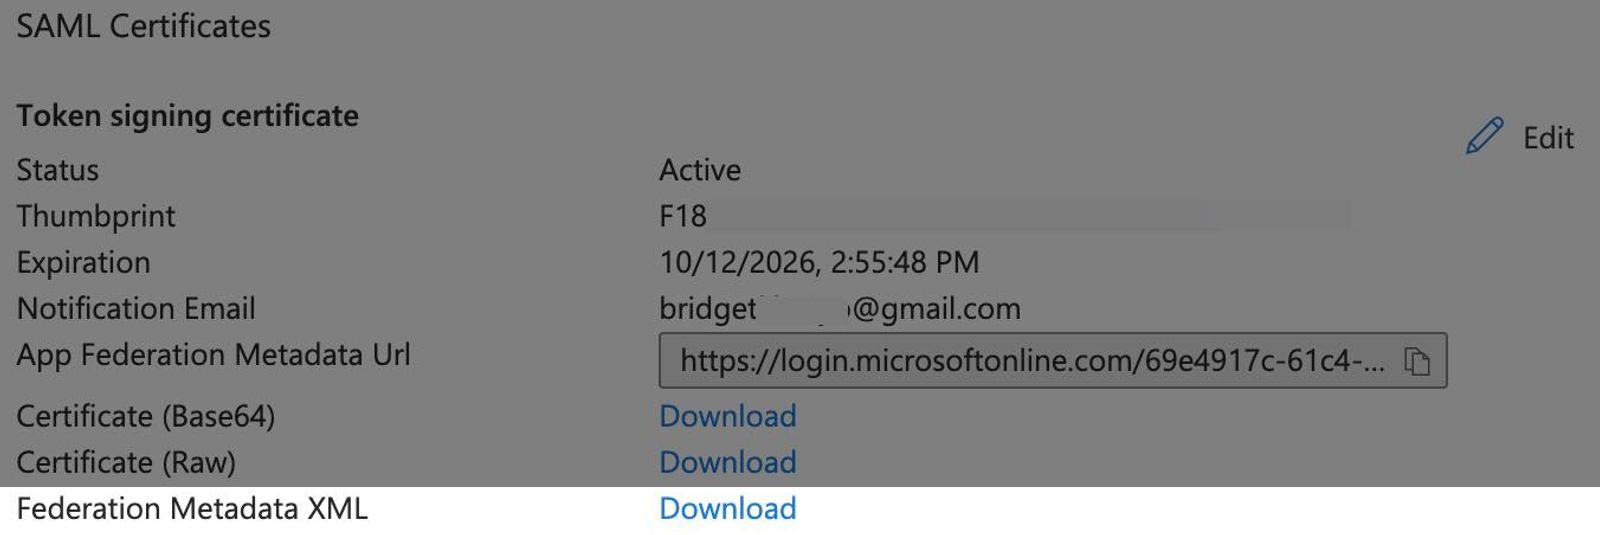
- Scroll down to the SAML Certificates box (step 3 on the Single sign-on page in Entra).
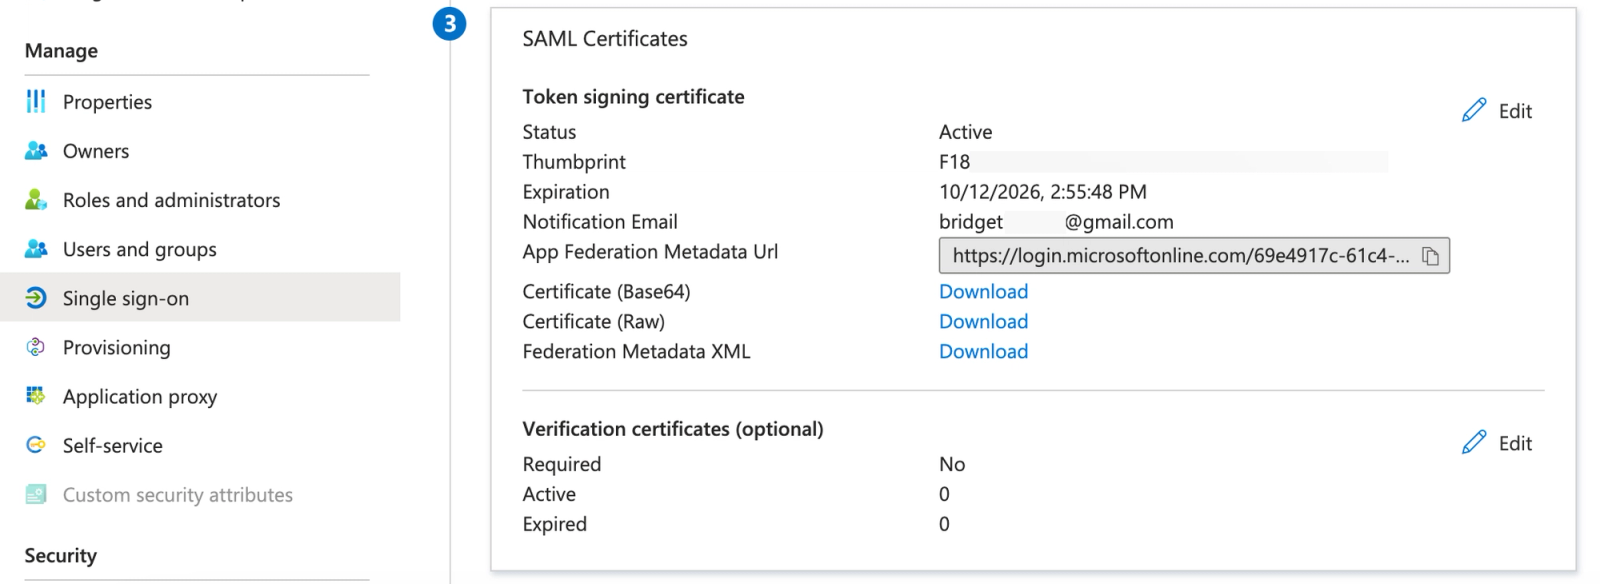
- Next to Federation Metadata XML, click Download.
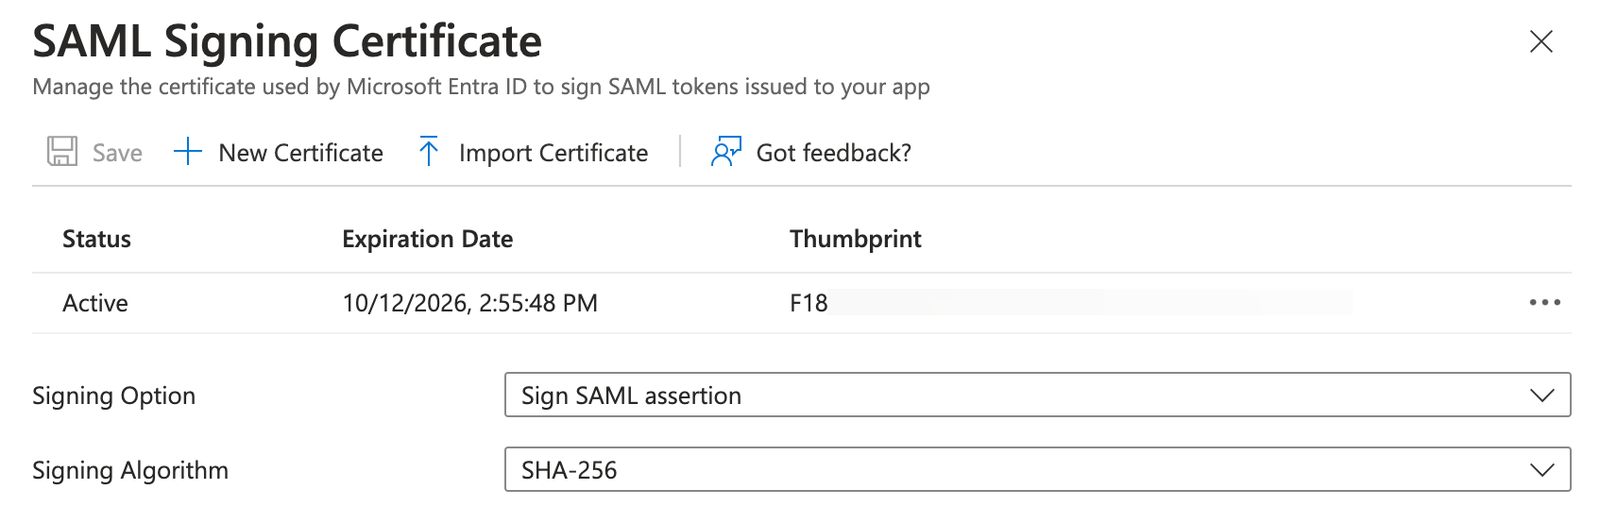
- Still within the SAML Certificates box, click Edit in the upper right.
- In the sidebar that appears on the right, check that the:
- Signing Option requires that the SAML assertion be signed (here, we set it to Sign SAML assertion). Note that signing the response is optional.
- Signing Algorithm is set to SHA-256.
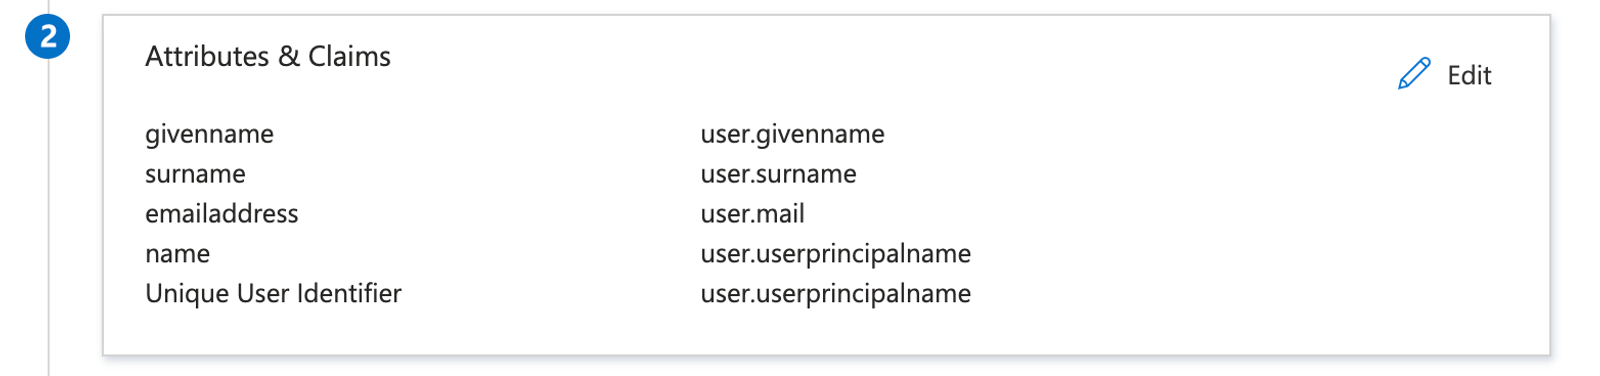
- Scroll back up to the Attributes & Claims box (step 2 on Single sign-on page in Entra) and click Edit.
- Click Unique User Identifier (Name ID) in the Required Claim section.
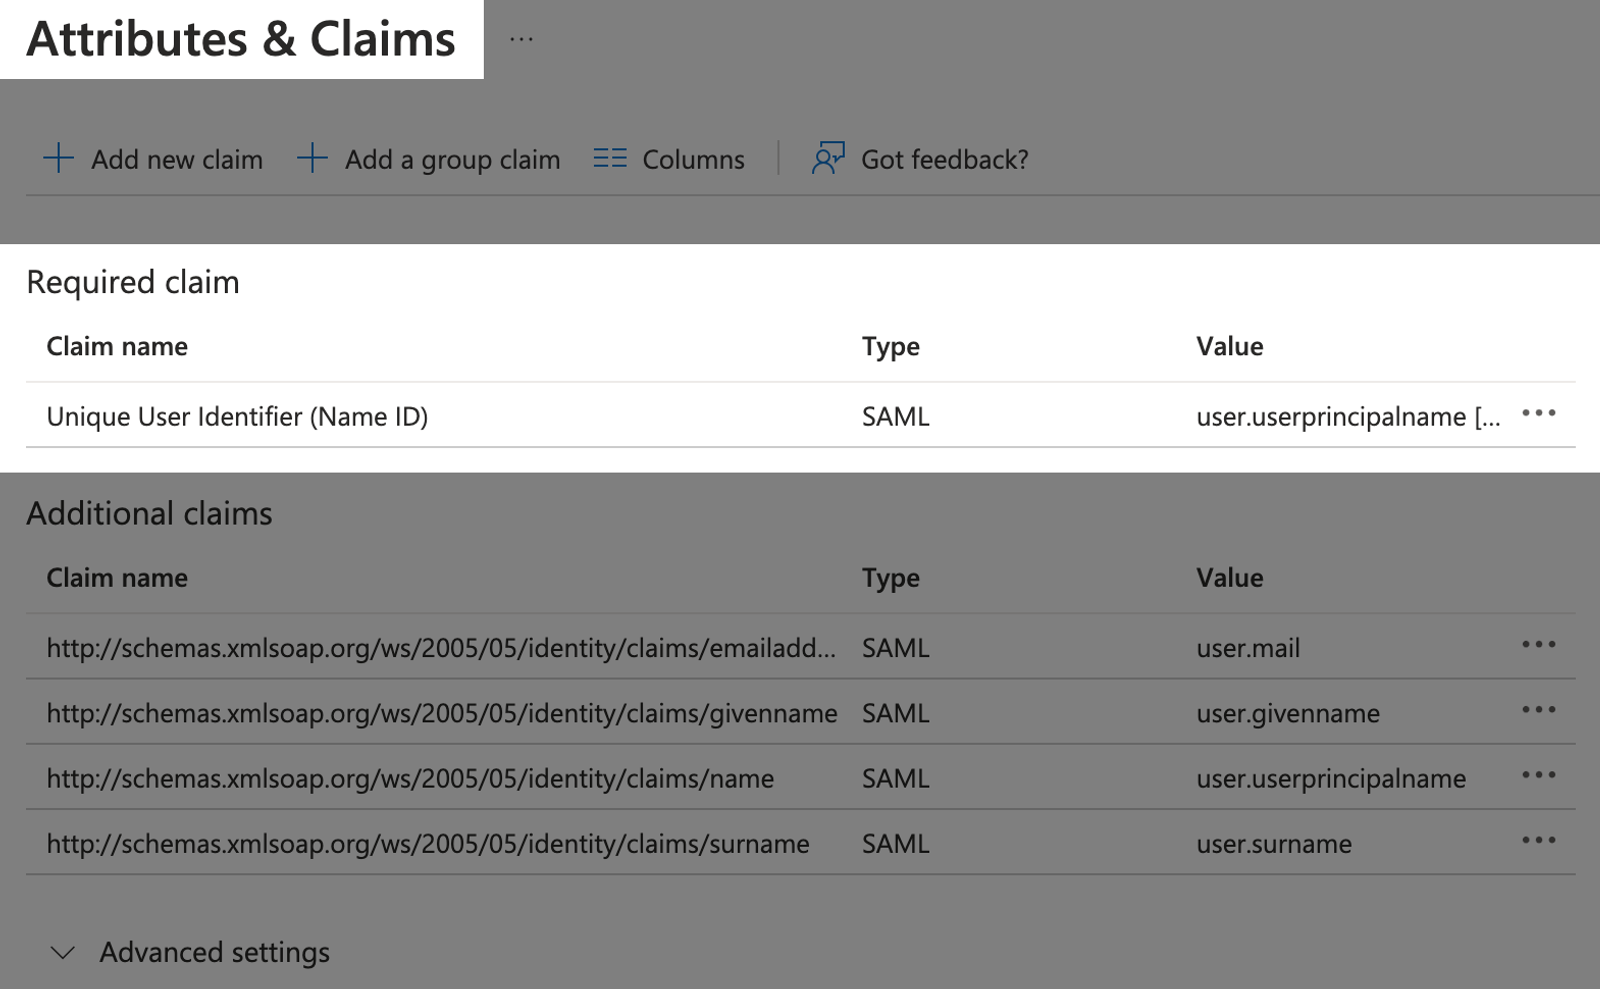
- Click the Source attribute dropdown.
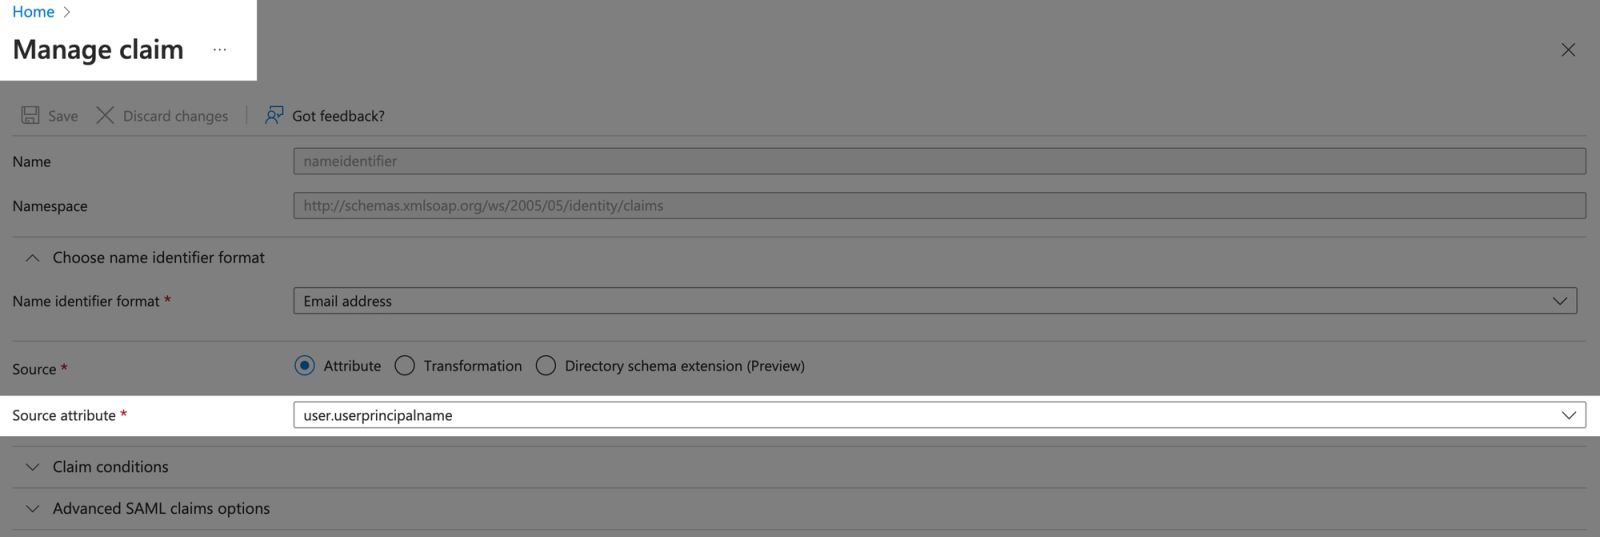
- Search for “user.mail” and then select it.
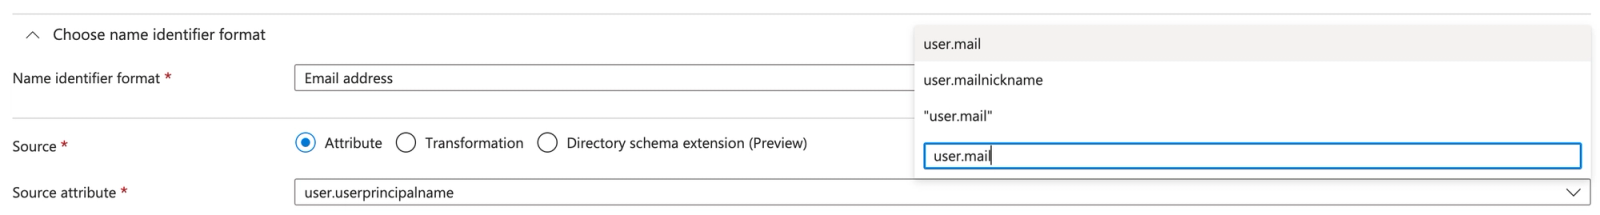
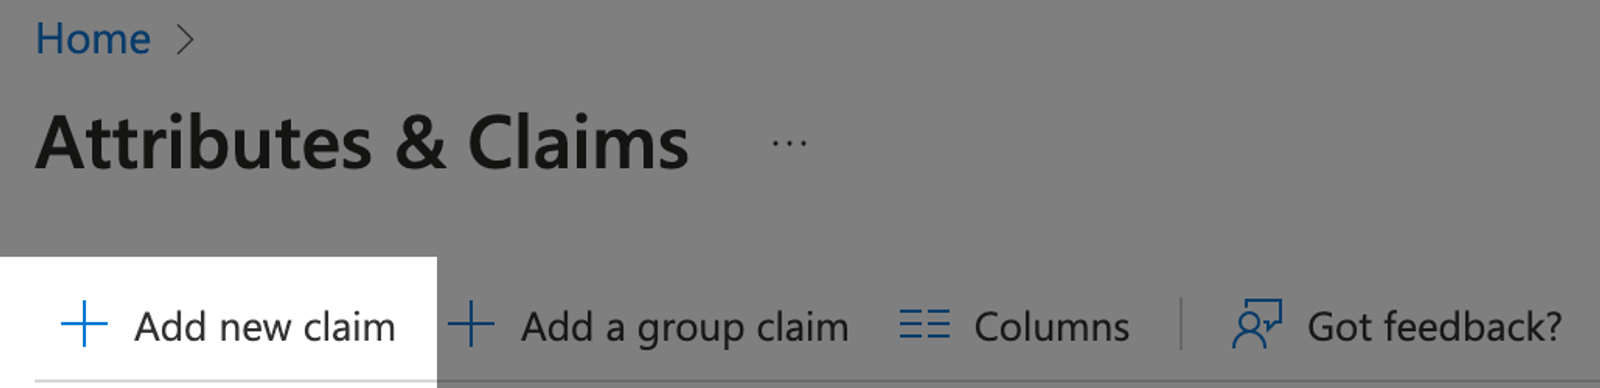
- Click Save in the upper left corner to go back to the Attributes & Claims page.
- Select Add new claim in the upper left.
- Enter “role” for the name.
- Change the Source attribute to "user.assignedroles."
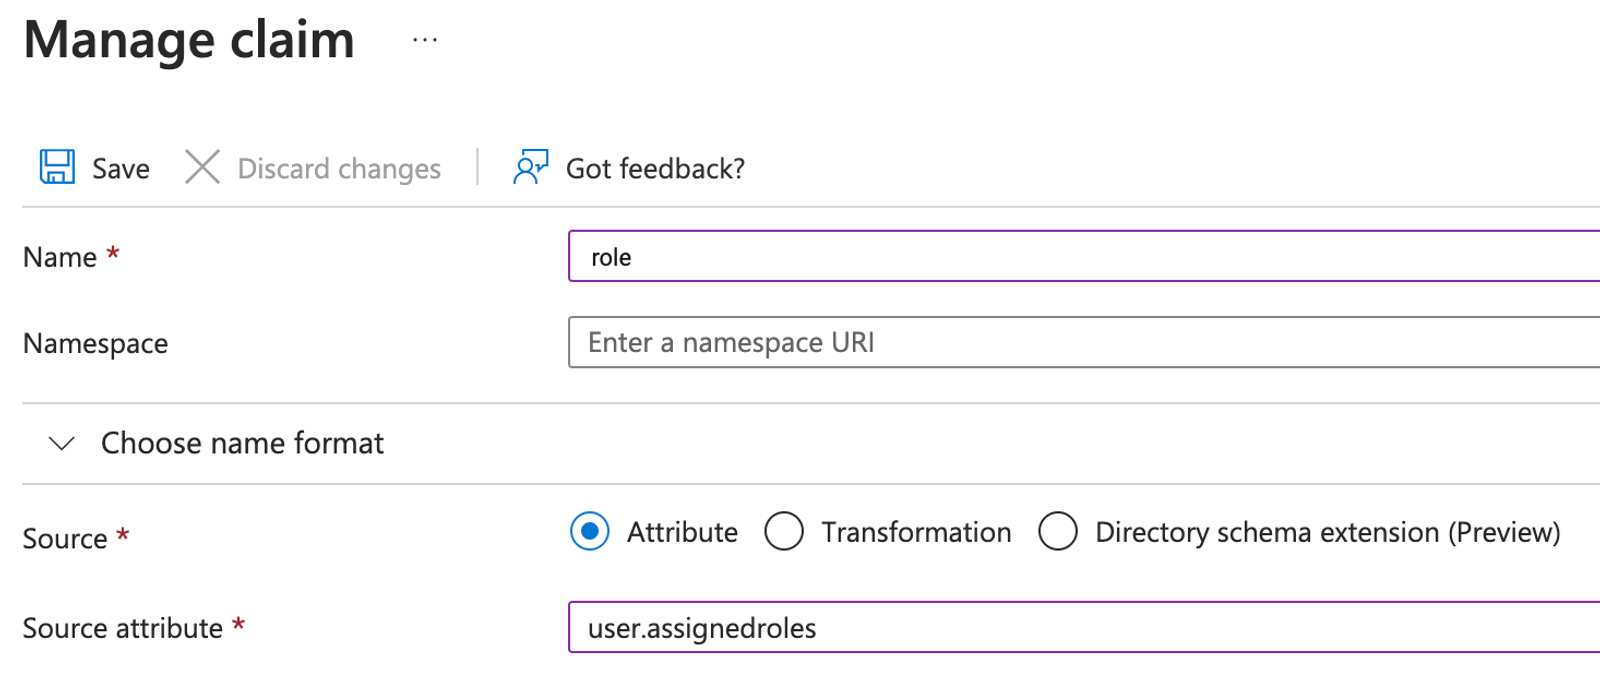
- Click Save.
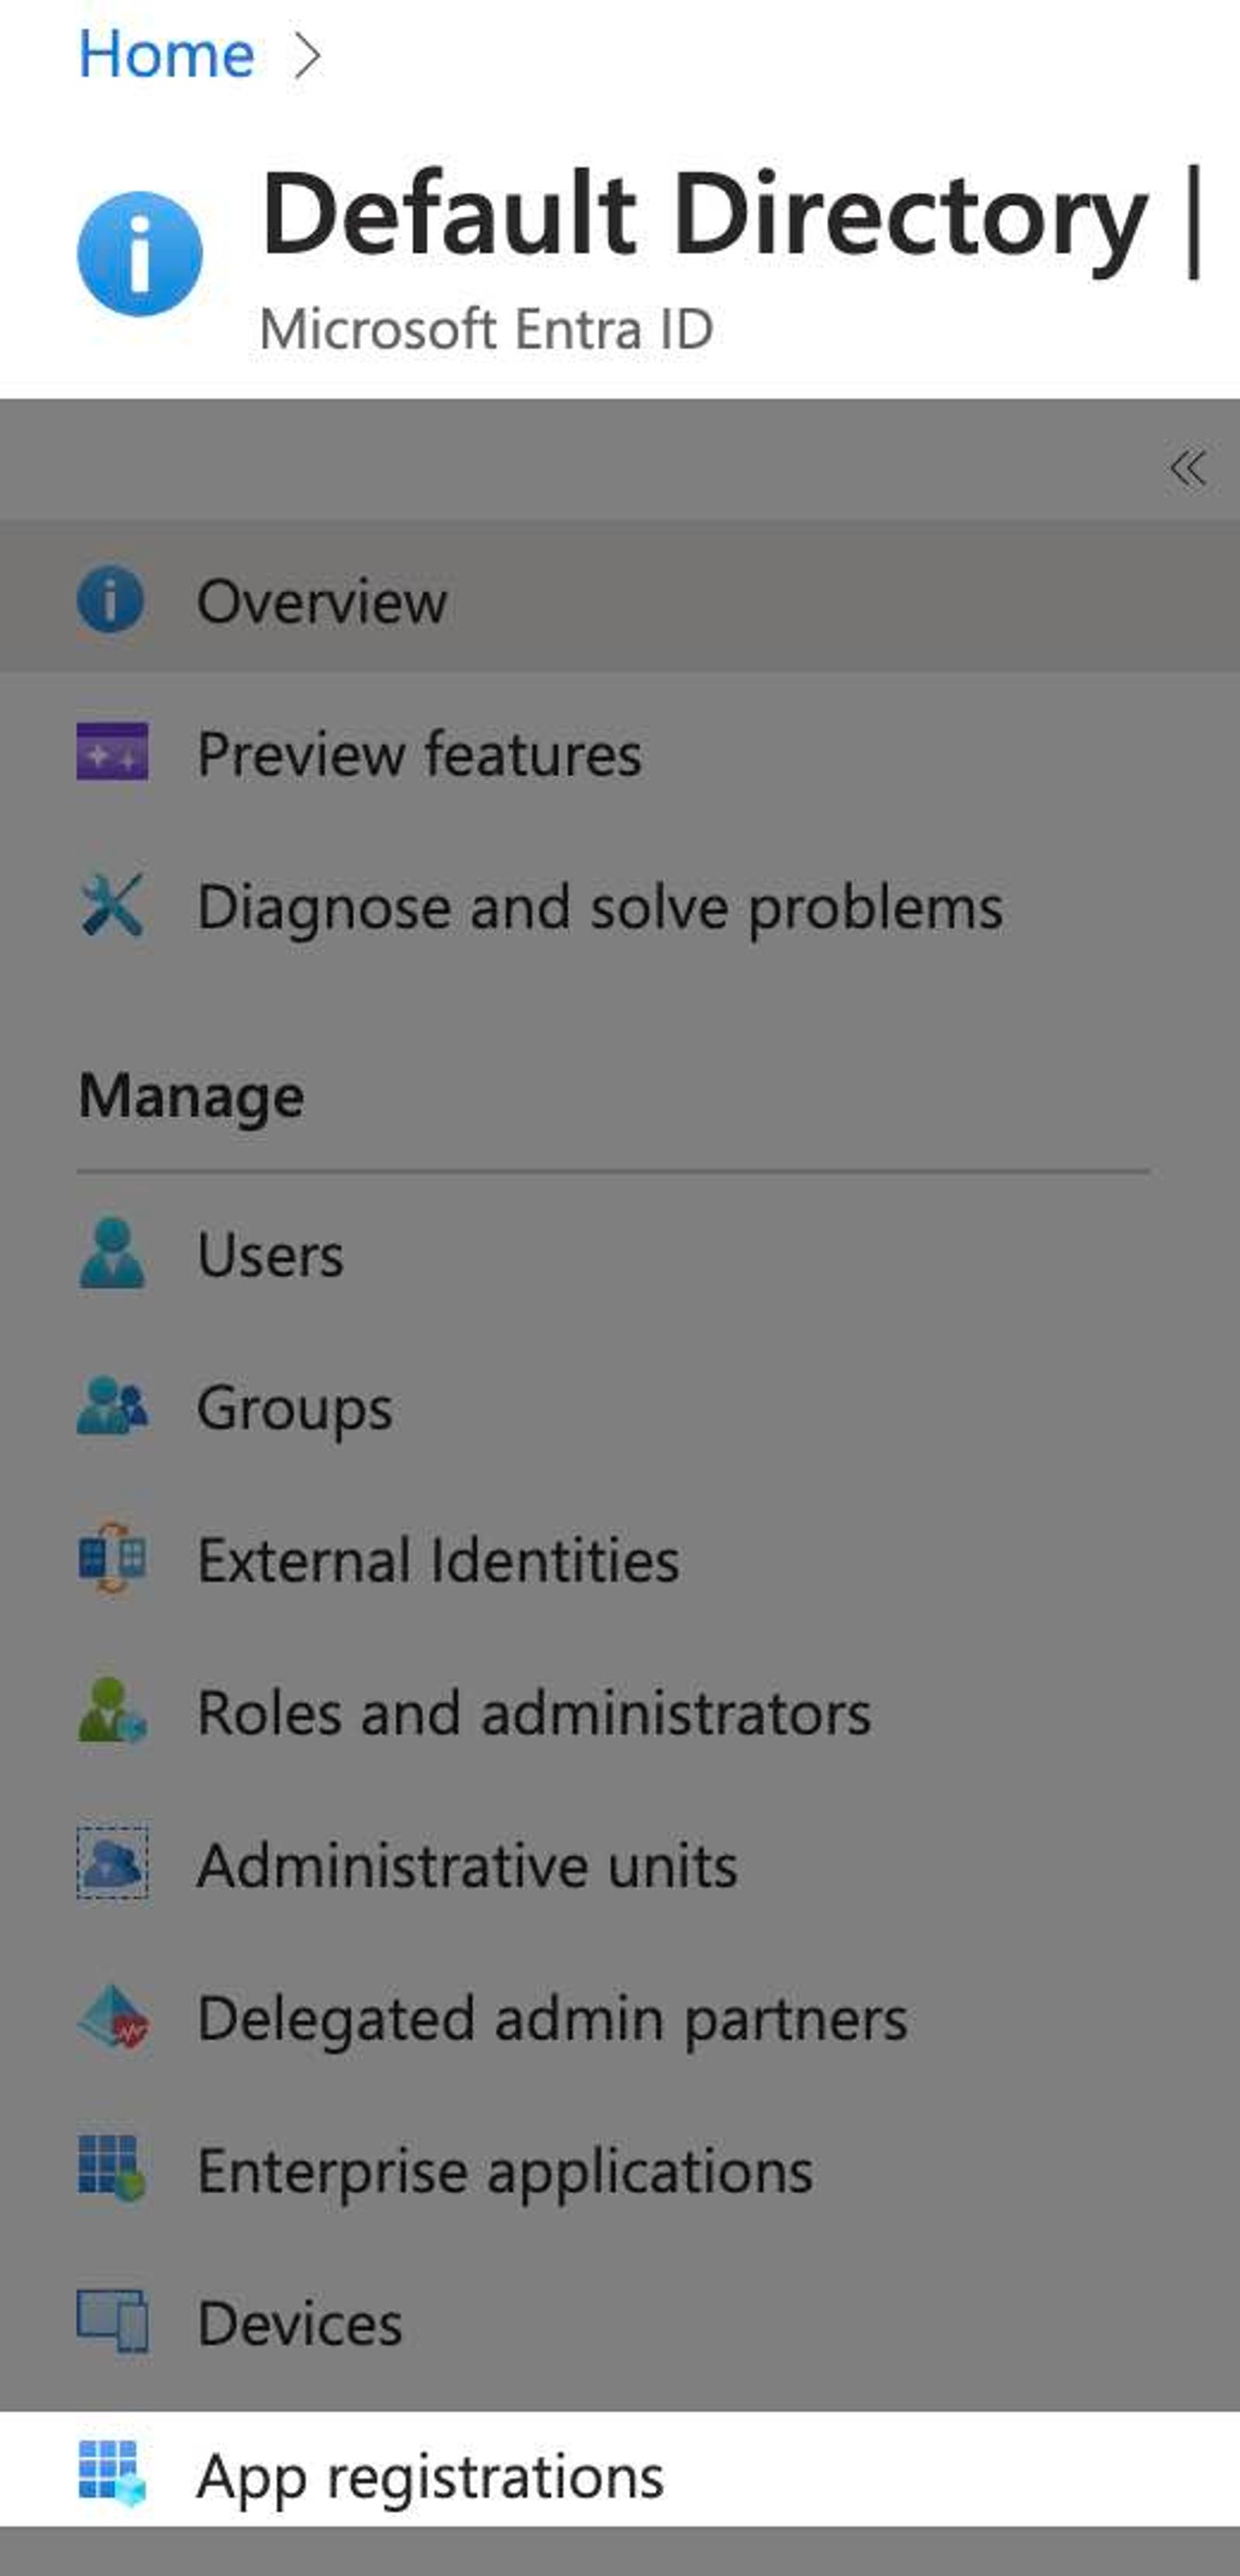
- Click Home to go back to the directory.
- In the left sidebar, click App registrations.
- Go to the All applications tab.
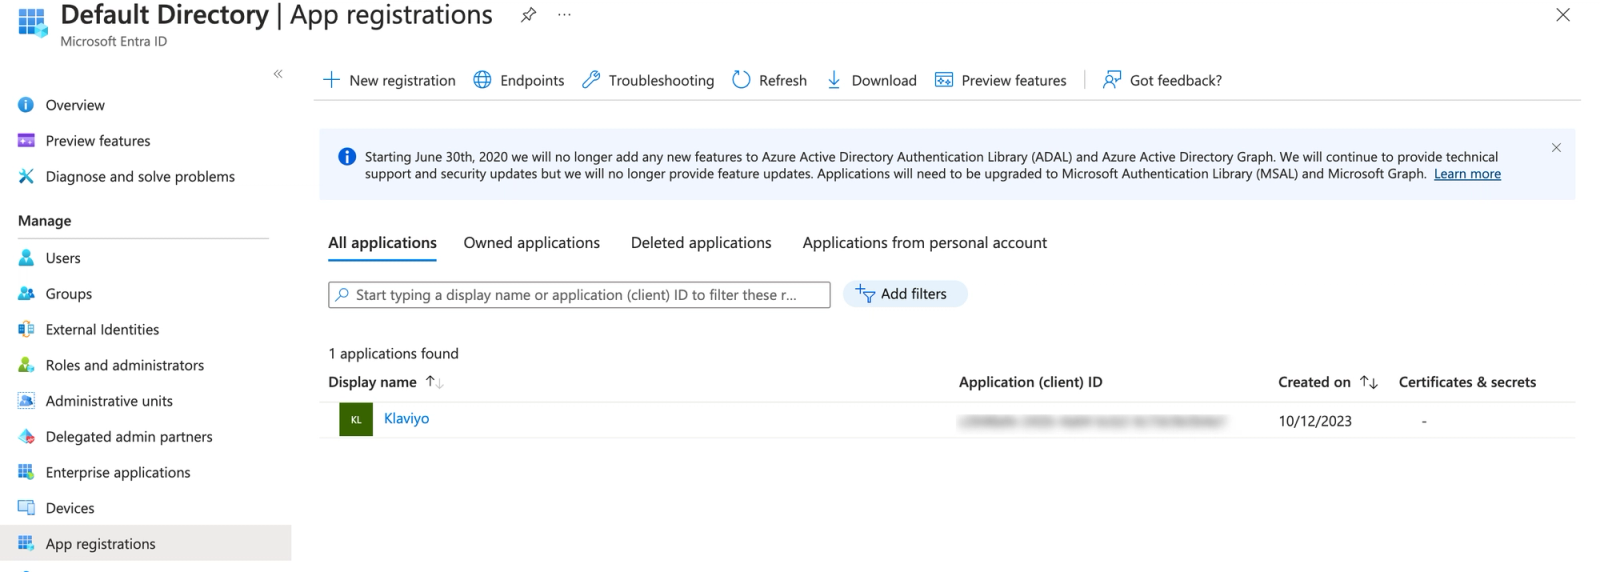
- Click into the Klaviyo app.
- Select App roles > Create app role.
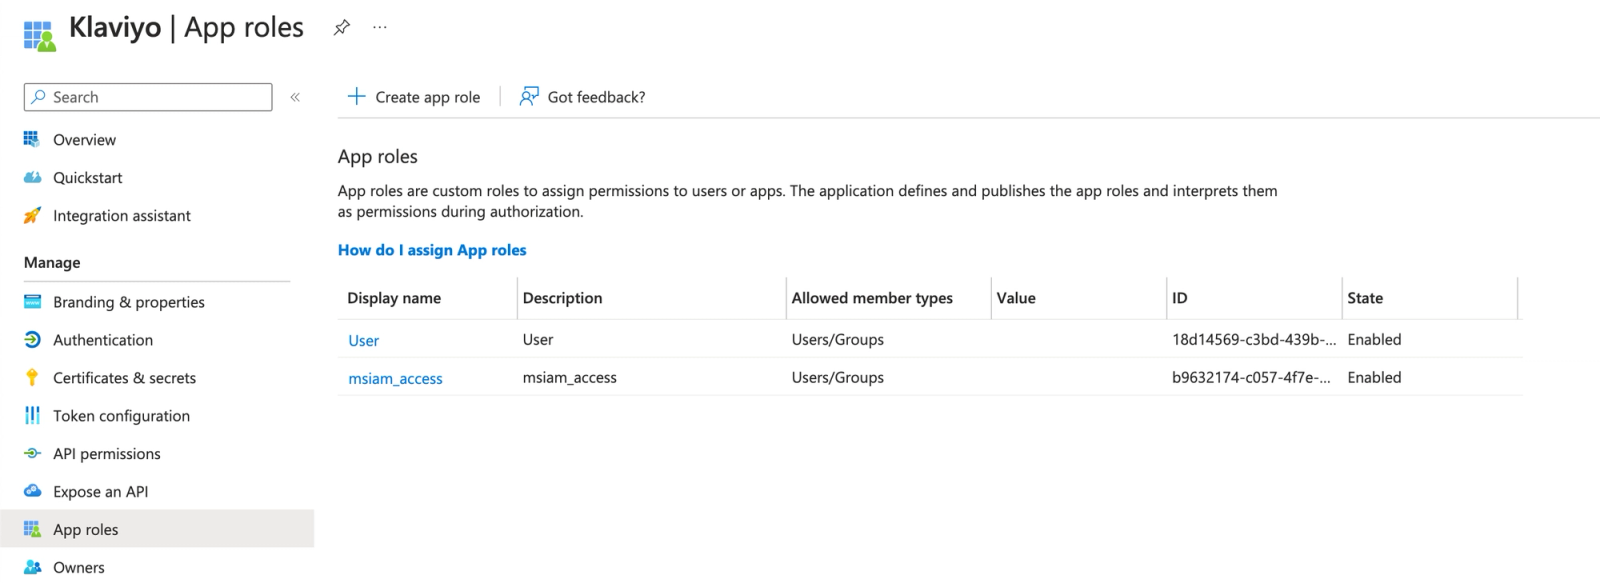
- Create the display name for each role.
- Select Users/Groups as the Allowed member types.
- For an account, assign one of the non-owner role values below exactly as shown. For a portfolio, use portfolio_admin, portfolio_manager, or portfolio_analyst instead. For the existing Owner, use owner or portfolio_owner as appropriate.
- admin
- manager
- analyst
- campaign_coordinator
- content_creator
- support
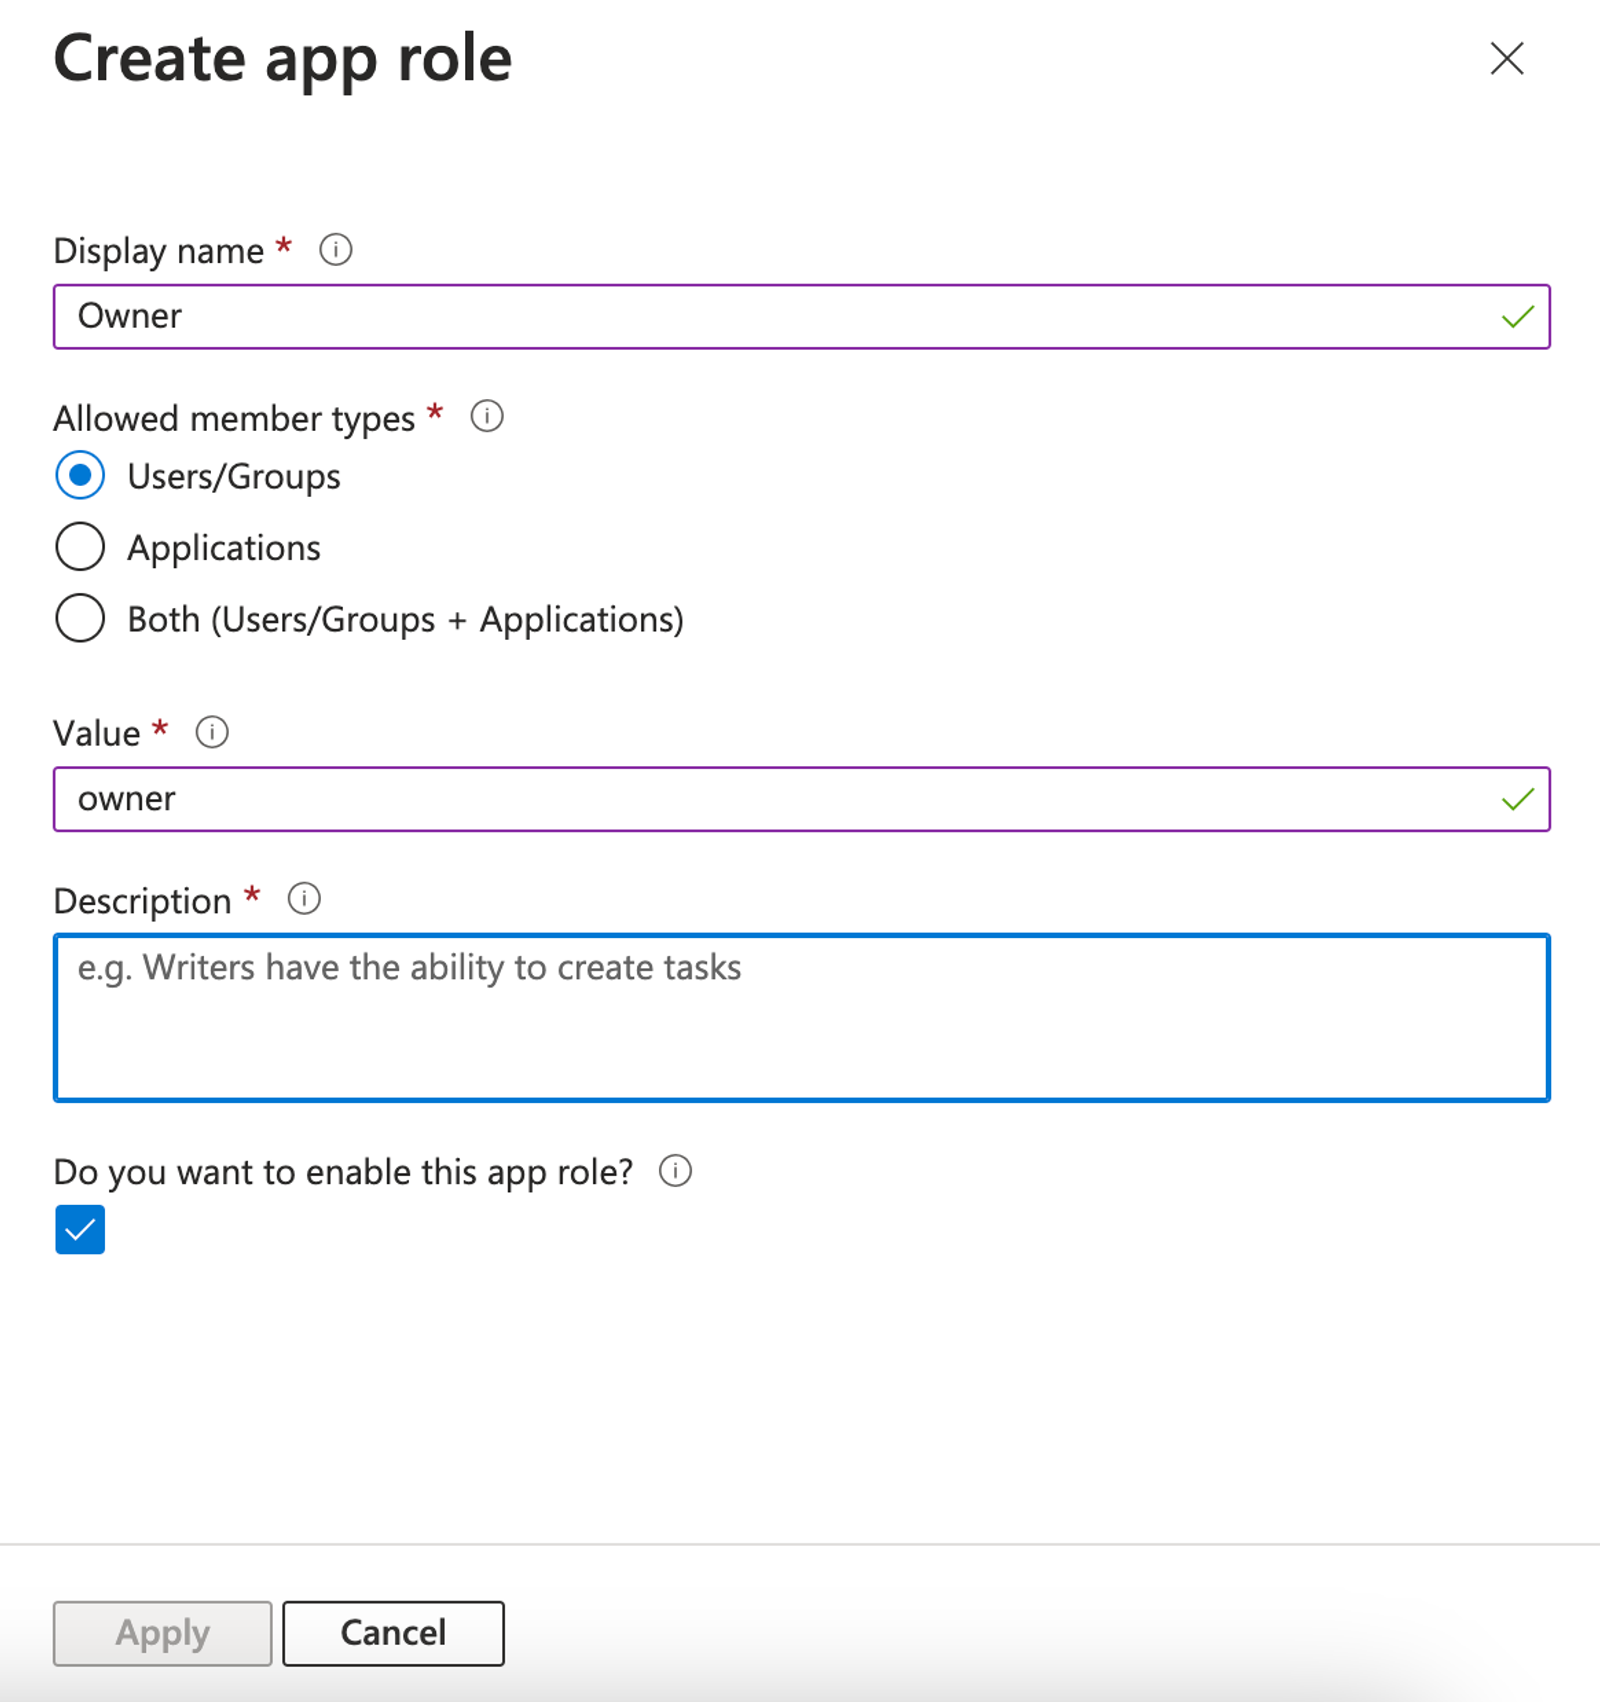
- Add a description, then click Apply.
Then, to assign users to the Klaviyo app, follow these steps:
- Navigate to Microsoft Entra ID > Enterprise applications.
- Click the Klaviyo app.
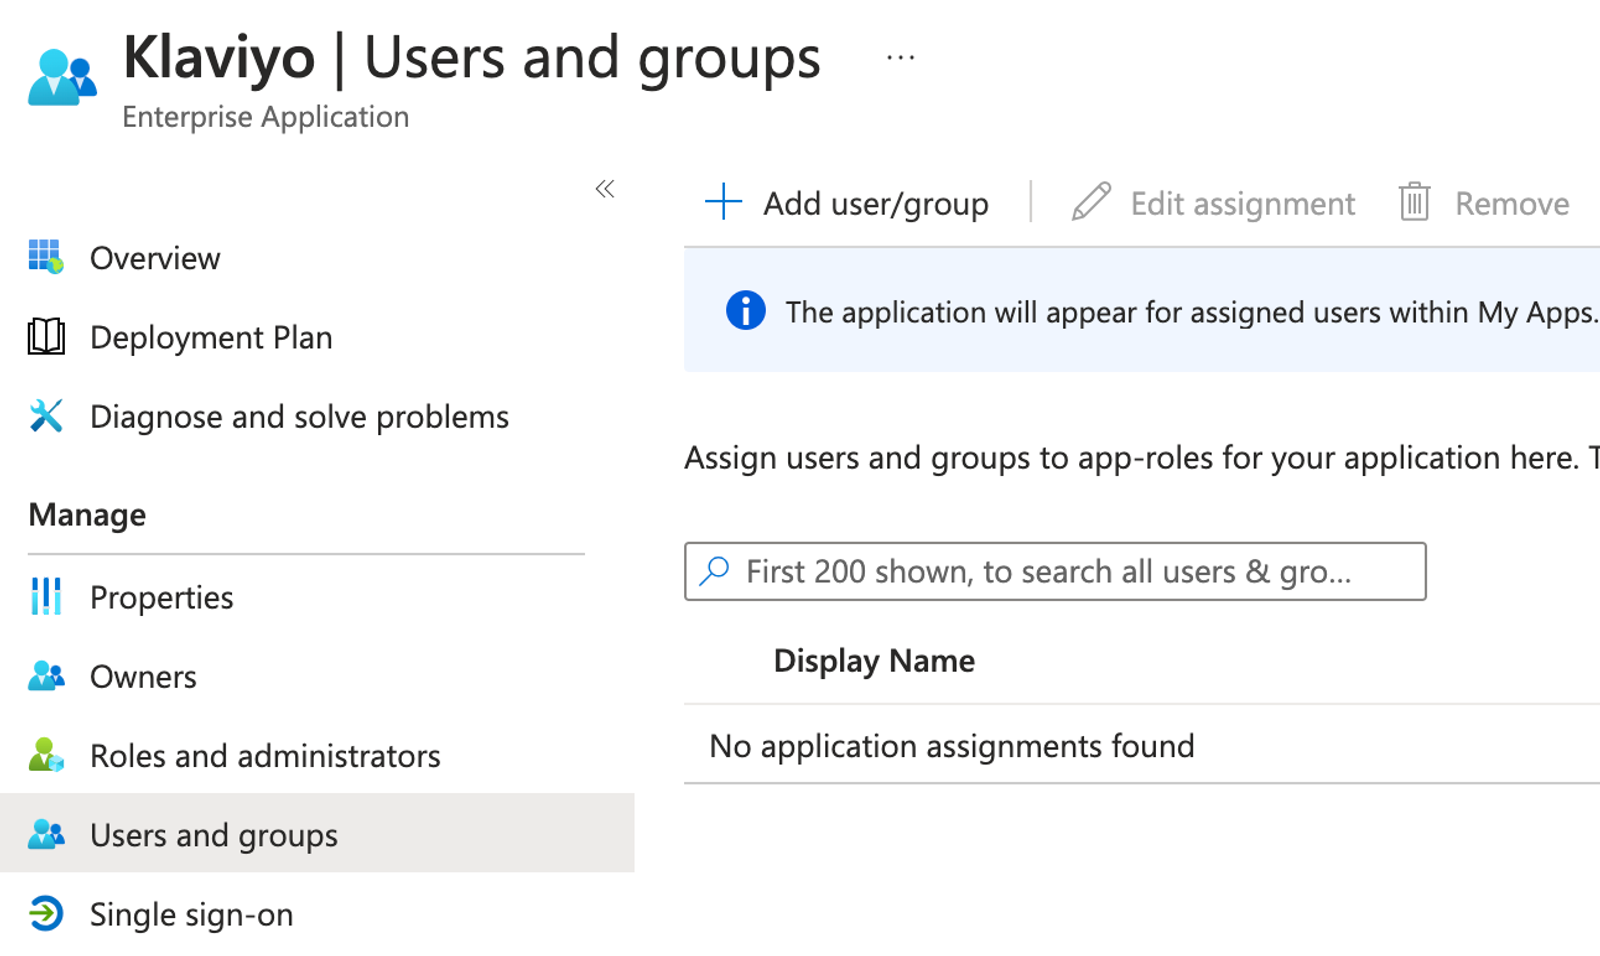
- Navigate to Users and groups > Add user/group.
- Click into Users to populate the right sidebar.
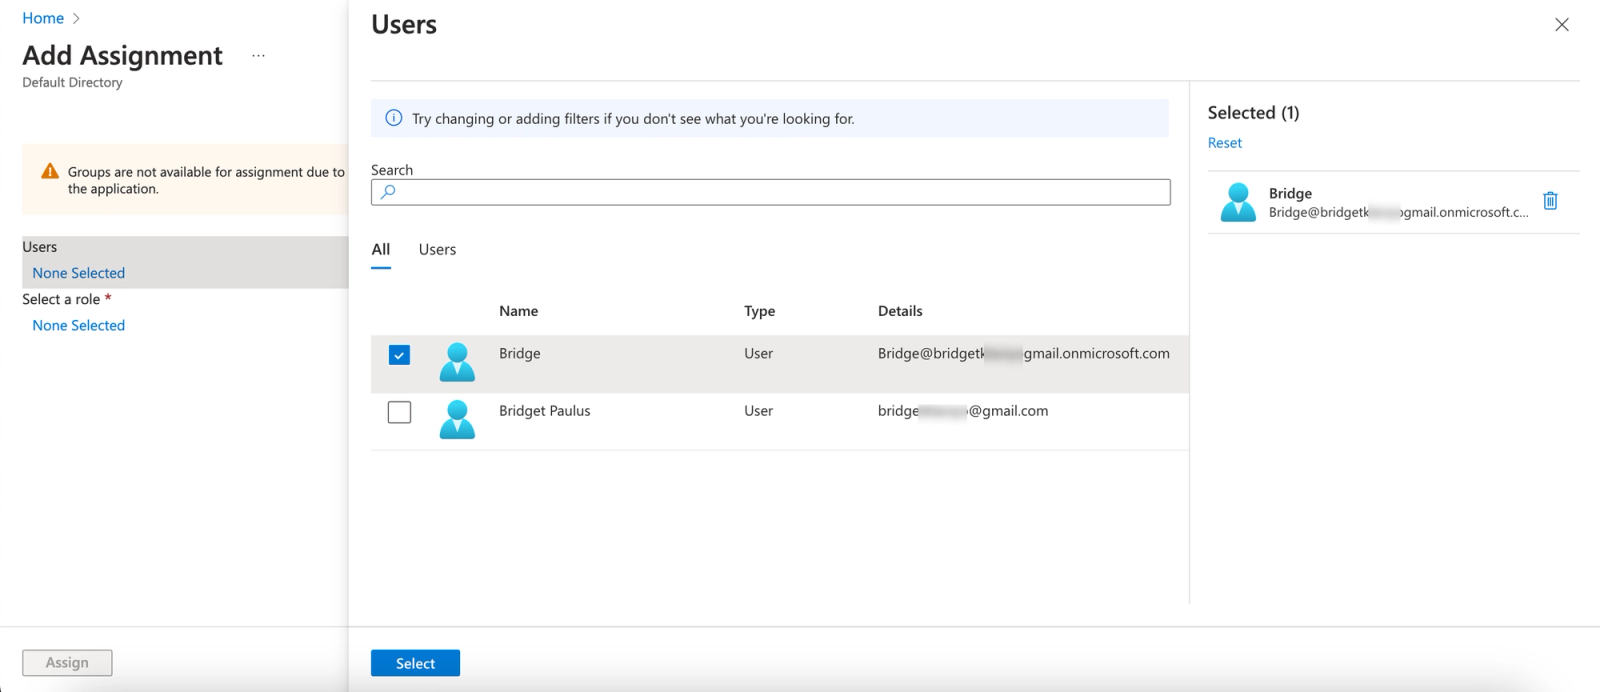
- Select the user(s) you want to add to the Klaviyo app.
- Click Select.
- Click into Select a role.
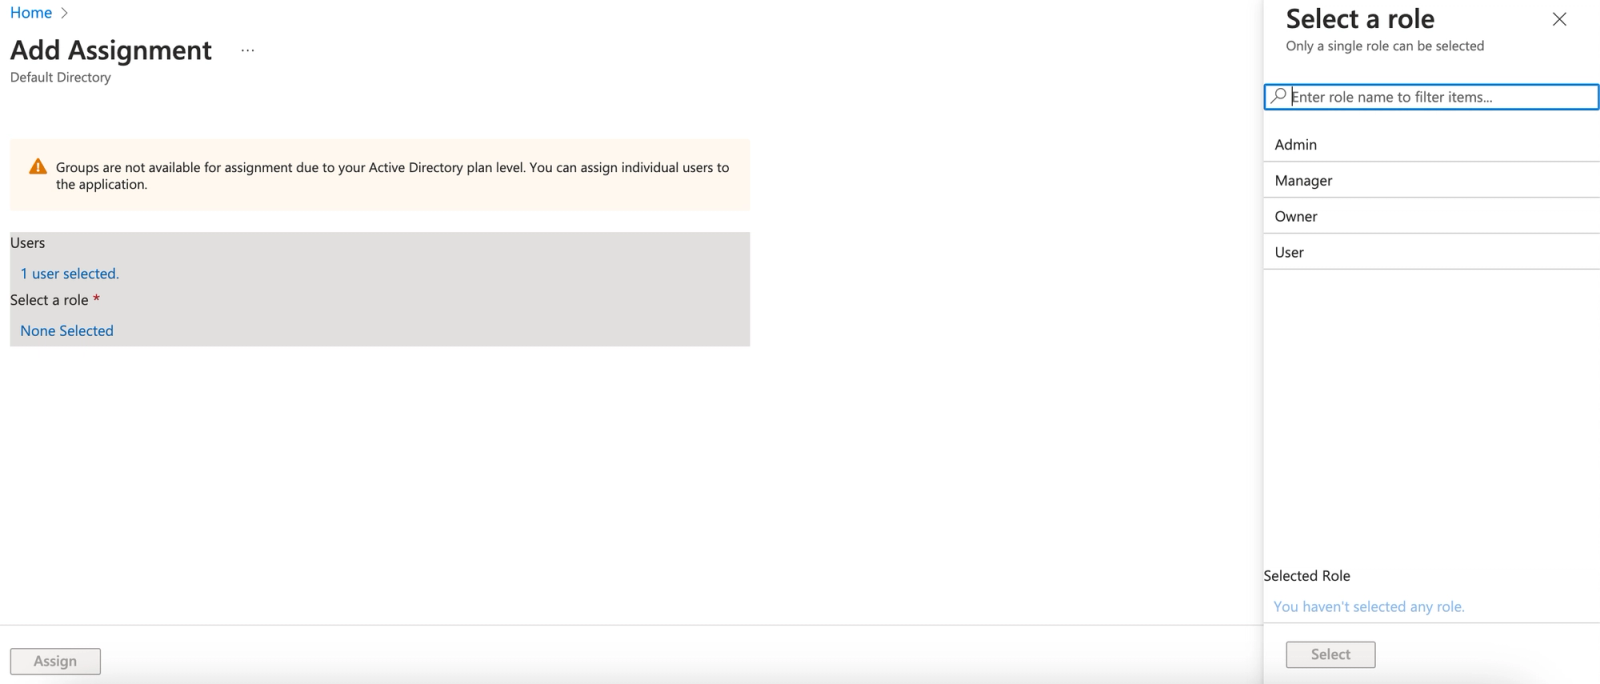
- Choose the role this user should have in Klaviyo.
- Click Select to confirm the role.
- Click Assign in the bottom left.
Finish setup in Klaviyo
- Navigate back to your Klaviyo tab to the Set up single-sign on (SSO) page.
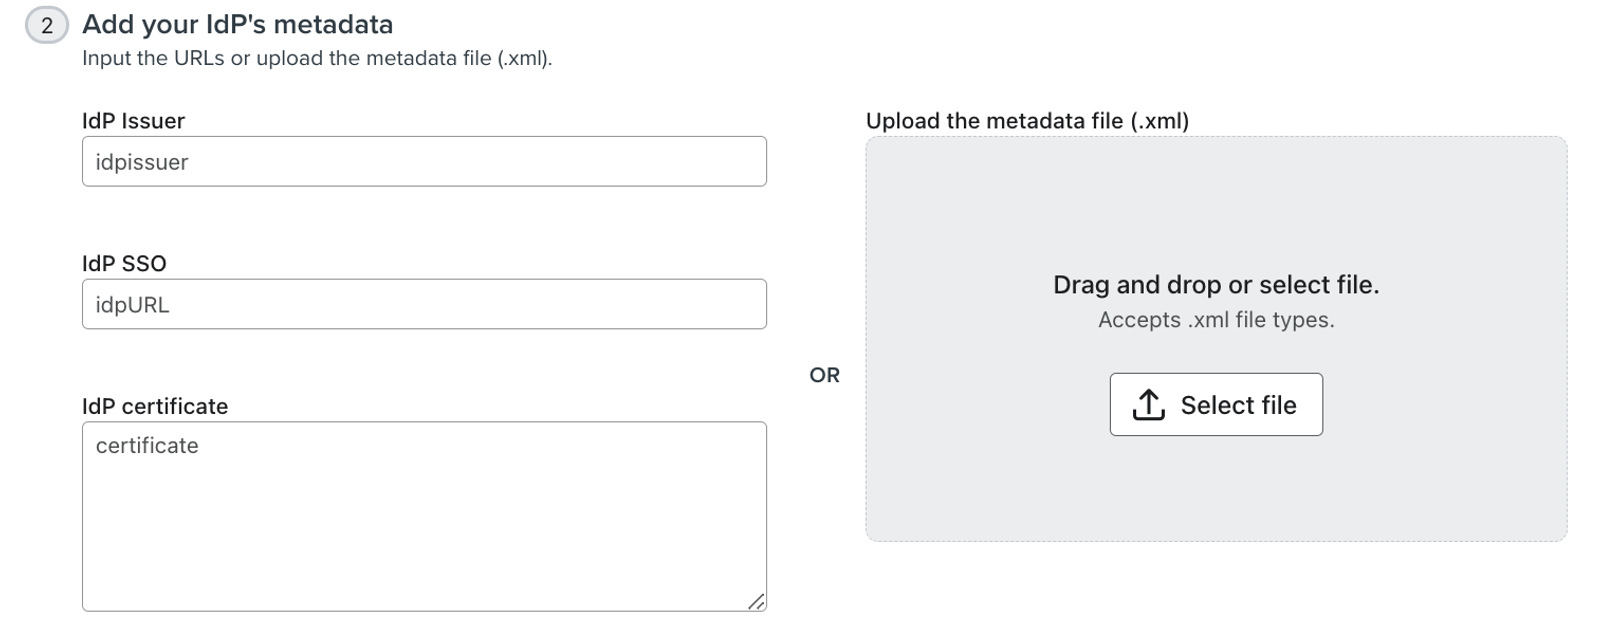
- Choose to either:
- Enter your IdP Issuer, IdP SSO URL, and IdP certificate manually.
- Upload your IdP’s metadata file (.xml) to fill in these fields.
- Create your SSO Login identifier (Workplace ID); often, this is the same name as your company.
- The ID must be unique and 3–63 characters long.
- The ID can contain only upper- or lowercase letters, numbers, hyphens (-), and underscores (_).
- The ID should be simple and easy for users to remember (such as your company name).
- For example, Klaviyo’s workplace ID is “Klaviyo.”
- Click Test SSO and complete the sign-in through your IdP. This saves your configuration and enables SSO.
- When the test succeeds, click Continue to return to Security. If it fails, correct the reported error and test again before proceeding.
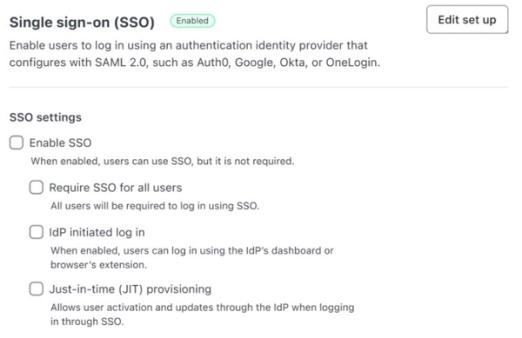
- Confirm that Enable SSO is selected. This allows SSO login but does not require it.
- Review the following settings. Changes save automatically. Turning a setting off opens a confirmation where you click Disable.
- Require SSO for all users: require SSO login for users who are not on the exemption list.
- IdP initiated log in: allow users to start SSO from their IdP’s dashboard or browser extension.
- Just-in-time (JIT) provisioning: create users and update their roles through the IdP when they log in with SSO. This is enabled for new configurations. If you turn it off, add users to Klaviyo before they try to log in.
Outcome
Now you'll be able to log in to Klaviyo using your SSO provider.
Additional resources
- Troubleshoot SSO and SCIM errors
Learn how to troubleshoot errors for single sign-on (SSO) with Klaviyo. This article is meant for those familiar with SSO, such as IT professionals.
- How to set up multi-factor authentication (MFA)
Learn how to set up multi-factor authentication (MFA) to help make your Klaviyo account or portfolio more secure. With MFA enabled, you sign in using a username and password, then verify your identity (such as by entering a code).
- How to set up SCIM user provisioning
Learn how to set up a system for cross-domain identity management (SCIM) user provisioning in an account or portfolio.